
About Pentest-Tools.com

Built by offensive security practitioners, Pentest-Tools.com gives security teams one place to test their defenses continuously, go deeper when needed, and prove what needs to be fixed.
Headquartered in Bucharest, Romania, we’ve been building and battle-testing detection, validation, and exploitation capabilities since 2017.
Today, more than 2,100 customers in 119+ countries use Pentest-Tools.com to test web apps, networks, and cloud infrastructure - and get evidence of what attackers can actually exploit.
Company facts
Founded
2017
Headquarters
Bucharest, Romania, Europe
Team
65+ specialists with backgrounds in cybersecurity, software development, business operations, and communications
Market reach
over 2,100 security teams in 119+ countries
Leadership
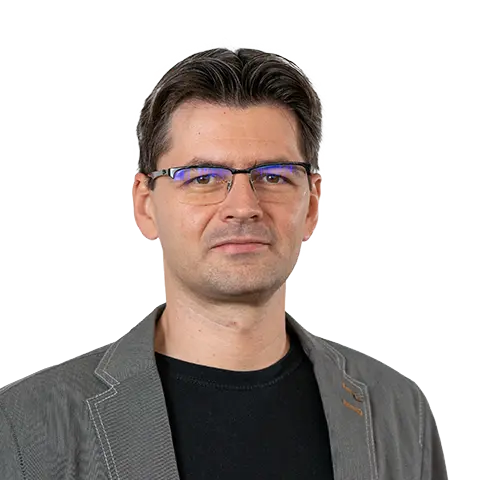
Adrian Furtuna
Founder & CEO
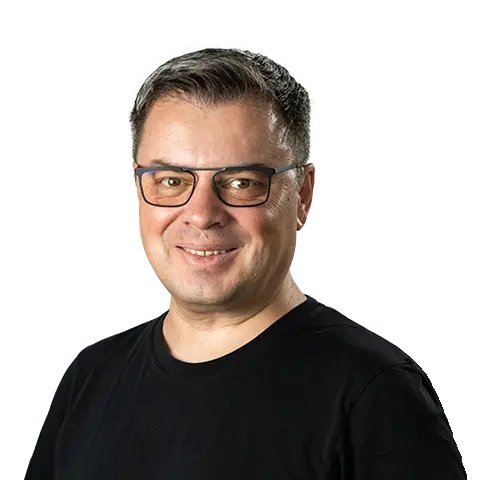
Andrei Pitis
Chairman of the Board
Diana Olar
Advisory Board Member
Why we built Pentest-Tools.com this way
Security teams rarely need the same testing depth for every target or situation. Sometimes they need continuous coverage and full control over testing. Sometimes a web app needs deeper, autonomous investigation they can get on the spot. And sometimes complex business logic or an independent assessment calls for human judgment.
We built Pentest-Tools.com so teams can choose the right testing mode without piecing together separate tools and vendors - while keeping the evidence they need to understand, prioritize, and communicate the results.
Security teams shouldn’t have to use the same testing approach for every situation. We want them to choose the right depth for the target, while getting evidence they can trust at every step.

Founder & CEO
Three ways to test, depending on what you need each day
Continuous vulnerability scanning & validation
Continuously test web apps, networks, and cloud infrastructure with deterministic scanning and validation. Control what gets tested, how, and when.
AI Pentests powered by Specter
Define the scope and let AI Pentests autonomously investigate a web app when you need more testing depth without waiting for the next manual pentest.
Human-led offensive security services
Bring in offensive security specialists when complex attack paths, business logic, independent attestation, or expert judgment matter.
Product facts
6+ million
scans/year
92%
detection precision
0 false positives
in AI Pentests powered by Specter
17,400+
detections & proprietary exploit modules
1 scan every 5s
for vulnerability detection & monitoring
315,000+ / year
unique web, network & cloud targets scanned
Evidence matters more than another alert
Finding a potential vulnerability is only the beginning. Security teams still need to determine whether it matters, what to fix first, and how to explain that decision to developers, IT, leadership, or auditors.
That's why we focus on evidence. When Pentest-Tools.com validates exploitability, we collect proof such as screenshots, data snippets, exploit output, and attack replay where available.
The result is a stronger basis for prioritization: not just what a scan detected, but what testing proved.
Not every detected vulnerability deserves the same attention. Proving exploitability gives security teams stronger evidence for deciding what to investigate and fix first.
Built from an attacker's perspective
Pentest-Tools.com started with offensive security practitioners building the tools they wanted to use themselves. That perspective still shapes how we build today.
Our offensive security practitioners, researchers, and customers continuously put the product through real testing scenarios. Their feedback helps us improve detection, validation, evidence, and reporting. Our research team also expands our vulnerability and exploit coverage as new vulnerabilities and attack techniques emerge.
The values that drive us
Ethics
White hats are all we wear. We are unflinchingly committed to ethical hacking both in terms of principles and practice. We do not encourage any unethical activities and behavior.
Integrity
We deliver on our promise, communicate transparently, and actively seek feedback from our customers. We treasure their trust and hold ourselves accountable for cultivating it.
Quality
We hate poorly written software and unreliable results. That is why we strive to create a product our customers can fully rely on. We use it ourselves daily and integrate feedback from customers in updates and new features.
Awards and recognition
Based on revenue growth

Companies to watch

Best Vulnerability Management Solution (highly commended)

G2 reviews
Unedited feedback from security practitioners who use Pentest-Tools.com for vulnerability assessment, validation, pentesting, and reporting.

A Swiss Army Knife for Quick and Deep Security Assessments
Swiss army knife tool for quick and deep security assessments.As an 5 years active user of the platform
I could certainly certify that pentest-tools.com it is a great tool for quick assessments of public facing systems. The added value came also from the fact that the internal systems can be assessed too via the VPN appliance.
Verified User in Airlines/Aviation
Source

Use cases
- Vulnerability scanning
- Internal scanning
Industry
Miscellaneous
Gartner Peer Insights reviews
89% of practitioners in large companies across IT services, Software, Energy & Utilities, and other sectors recommend Pentest-Tools.com.
Reliable intel and fast export features enhance penetration testing workflow
Easy to use, great reliable and accurate intel and reporting. The ability to export reports to editable formats saves a lot of time and provides extensive detail on the tests performed. It is fast and scalable, ensuring my work as a pen tester is automated to free up time for the mundane admin tasks that normally waste time. The remediation guidance helps my clients to get the vulnerabilities and the remediation actions done in a shortened time frame. It is a valuable portal to increase productivity and add more profit. Attack simulations and automated bots make test scheduling and exposure assessments a breeze.
Chief Information Security Officer
Source
Use cases
- Pentest reporting
- Automation
- Vulnerability management
Industry
IT & Services
How we got here
2013 - A server on a balcony
Ten years into pentesting at a Big Four company, our founder - Adrian Furtuna - got tired of tools that couldn't prove anything, so he built his own on an always-on Pentium 4 desktop running Debian.
2017 - A side project becomes a company
A stranger paid for it, which meant the frustration wasn't just Adrian's. He formed the first team, entered the Innovation Labs accelerator, and won the Grand Prize.
2020 - A brand-new DAST tool
At the time, our Website Scanner had accuracy problems we couldn't engineer around, so we rebuilt from scratch. Detection was never the end goal, though. Validation was.
2020 - Repeatable offensive workflows
Pentest Robots launched at Black Hat Europe, chaining recon, scanning, fingerprinting, detection, and exploitation into one assessment. One connected testing flow, so output from each step flows into the next.
2021 - Sniper - proof instead of probability
2026 - Autonomous testing depth
AI Pentests powered by Specter launched at DEF CON 34 and added autonomous investigation alongside deterministic scanning and human-led testing. External validators give every AI result a second opinion, because confidence without proof is the problem we set out to solve.
Get in touch for media requests
Looking for a dedicated quote, to do an interview or simply interested in more details about Pentest-Tools.com for your article or report? Send us an email and we'll be in touch right away!

Andra Zaharia
Head of Marketing
Communication specialist with a decade of experience in cybersecurity.
I strongly believe in serving the infosec community through ethical marketing that builds bridges across people, organizations, and industries. I stick to the point and prefer a hands-on approach.
Student of the hacker mindset. Adamant about using the right words and fighting against infosec marketing clichés.
See what you can do with Pentest-Tools.com
Test continuously, investigate deeper on-demand with AI, and bring in human expertise when the situation calls for it - with evidence that helps your team decide what to fix.
