Changelog

These are the latest updates we've made to our platform. If you have any questions about any of the updates you see below, please feel free to contact us!

Date

August 2026

  1. 155 new detections added to the Network Scanner, 70 of them critical

    Copy link to “155 new detections added to the Network Scanner, 70 of them critical”

    The Network Scanner gained 155 new detections in August, 70 of them critical, prioritized by CVSS, EPSS, and CISA KEV.

    The most notable:

    ◉ JetBrains TeamCity < 2026.1.3, 2025.11.7, remote code execution (CVE-2026-63077)

    ◉ Metabase, unauthenticated SQL injection (CVE-2026-72898)

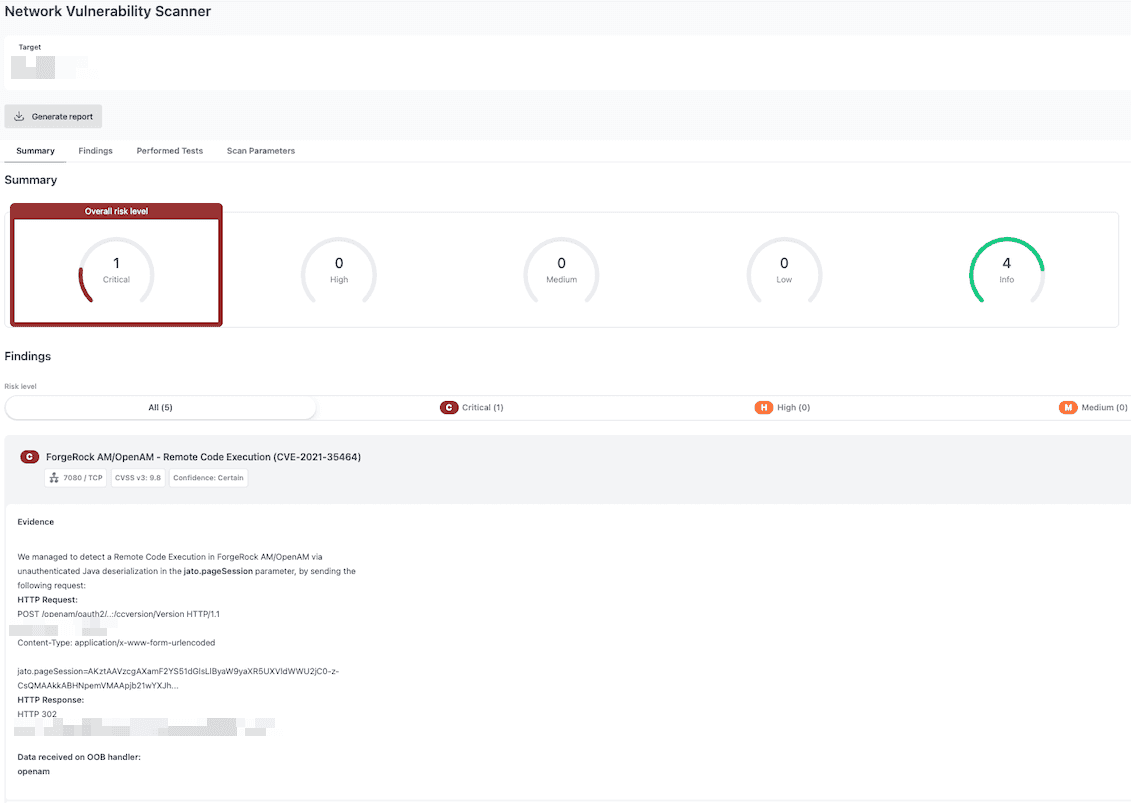
    ◉ ForgeRock AM/OpenAM, remote code execution (CVE-2021-35464)

    ◉ Cisco ISE < 3.4P2, unauthenticated arbitrary file upload (CVE-2025-20282)

    Why it matters

    Coverage that lands within days of disclosure is the difference between finding an exposure yourself and reading about it in an incident report.

    How to use

    Run a scan to check your targets, then put the high-value ones on scheduled monitoring so new coverage applies automatically as it ships.
    Scan your targets

  2. Sniper adds an exploit for a Forgerock OpenAM RCE still active in the wild (CVE-2021-35464)

    Copy link to “Sniper adds an exploit for a Forgerock OpenAM RCE still active in the wild (CVE-2021-35464)”

    Sniper Auto-Exploiter added a new exploit module this month for CVE-2021-35464, a remote code execution vulnerability in Forgerock OpenAM.

    The CVE has been public for years, but it's still showing up in live environments, which makes it a good reminder that "old" and "settled" aren't the same thing. Detection is now live in the Network Scanner as well.

    Why it matters

    A five-year-old CVE still causing damage is exactly the kind of exposure that slips through when a scan schedule assumes older vulnerabilities are already handled. Sniper turns the finding into exploit-backed evidence instead of a CVSS score on a slide.

    How to use

    Run Sniper against a confirmed target to generate exploit-backed evidence. As always, if Sniper can exploit it, the Network Scanner can detect it.

    Prove it with Sniper

November 2025

  1. Exploitation for CVE-2020-36847 (Remote Code Execution in Wordpress Simple File List plugin)

    Copy link to “Exploitation for CVE-2020-36847 (Remote Code Execution in Wordpress Simple File List plugin)”

    We’ve added an exclusive exploit for CVE-2020-36847 (WordPress Simple File List - Unauthenticated RCE) into Sniper, so you can move from suspicion to proof of rce in a controlled, ethical way.

    Why it matters
    CVE-2020-36847 is a critical, unauthenticated Remote Code Execution vulnerability in the Simple File List plugin for WordPress. Versions up to and including 4.2.2 let an attacker upload a php payload disguised as an image, then use the plugin’s rename function to change the extension to .php and run it on the server. The result is full arbitrary code execution with no login required, a fast path to site takeover, database access, credential theft, and lateral movement if the host can reach internal services. Updating to 4.2.3 or later fixes the issue.

    How to use

    Validate in Sniper → capture RCE evidence safely → patch the plugin (4.2.3+) → re-run Sniper to confirm remediation and rule out other exposed sites using the same plugin.

  2. Detection & exploitation for the React Native Community CLI development server RCE (CVE-2025-11953)

    Copy link to “Detection & exploitation for the React Native Community CLI development server RCE (CVE-2025-11953)”

    We’ve just added an exclusive exploit for CVE-2025-11953 (React Native Community CLI development server) into Sniper and paired it with Network Scanner detection, so you can spot and confirm this RCE in one workflow.

    Why it matters
    CVE-2025-11953 is a critical, unauthenticated Remote Code Execution issue in the Metro development server started by the react native community cli. The server exposes an endpoint vulnerable to os command injection, letting an external attacker run arbitrary commands on the host if the dev server is reachable over the network. With a CVSS of 9.8, the impact is full compromise of the dev server environment and whatever credentials, source code, or internal network access it can reach.

    How to use

    Detect with the Network Scanner → validate in Sniper → re-scan to confirm remediation and catch leftover exposure across other hosts running the Metro dev server.

  3. Detection & exploitation for the Oracle RCE (CVE-2025-61882)

    Copy link to “Detection & exploitation for the Oracle RCE (CVE-2025-61882)”

    We’ve just added an exclusive exploit for CVE-2025-61882 (Oracle E-Business Suite BI Publisher RCE) into Sniper and paired it with Network Scanner detection - available exclusively to Pentest-Tools.com customers.

    Why it matters
    This vulnerability is a critical, unauthenticated, pre-auth Remote Code Execution in Oracle EBS (versions 12.2.3 → 12.2.14). It has a CVSS of ~9.8 and is actively exploited in the wild. It allows remote attackers to run arbitrary code and potentially take over the Concurrent Processing subsystem, often containing high-value ERP, payroll, and financial data. This module gives you fast detection and zero-guesswork validation in one place.

    How to use

    detect with the Network Scanner → validate in Sniper → re-scan to confirm remediation and rule out residual exposure across multiple assets.

March 2024

  1. Don’t miss a thing with new detection modules in the Network Scanner

    Copy link to “Don’t miss a thing with new detection modules in the Network Scanner”

    Thanks to our security research team, you can now detect:

    Speaking about Roundcube, a couple of months ago we published an analysis - and public exploit - for CVE-2021-44026, an SQL injection vulnerability in the open-source mail client.

    The Network Scanner now also generates explicit findings for sensitive services that shouldn't be exposed on the internet (e.g. SMB, RDP, MySQL), which are easier to include in your reports.

January 2024

December 2023

November 2023

October 2023