

Search • Page 4/6
72 results for "unauthorized access"
Security research
How to manually detect CVE-2022-21371 in Oracle WebLogic Servers
If you’re constantly thinking about better ways to discover critical vulnerabilities in systems, you are not alone. As a security researcher, I spend most of my time understanding their root cause and their potential impact on organizations, striving to help other security specialists communicate them effectively.

- Author(s)
- Published at
- Updated at

Platform updates
April updates: Get RCE evidence for 6 critical CVEs
After weeks of working on auto-exploitation for this critical CVE (CVSSv3 9.8), we finally have it! As a Pentest-Tools.com customer, you can run Sniper Auto-Exploiter to get conclusive proof that validates targets vulnerable to this high-risk vulnerability, which bad actors have already shown interest in.
- Author(s)
- Published at
- Updated at
Security research
How to exploit Zabbix Unsafe Session Storage (CVE-2022-23131)
Due to its increasing popularity and administrative access to most companies’ infrastructure, Zabbix has become a high-profile target for threat actors. So of course a security issue like the Unsafe Session Storage vulnerability attracts motivated cybercriminals. If it’s up to you to find exploitable targets and gather proof for vulnerability validation for your ethical hacking engagements, this guide is for you!
- Author(s)
- Published at
- Updated at

Security research
How to detect and exploit Citrix ADC and Citrix Gateway (CVE-2020-8194)
Citrix systems are very popular, even famous, one could say. They even sponsor Formula 1 teams! But despite their notoriety, they use the FreeBSD OS on their devices and plain PHP for web services, so I got easy access to the code and analyzed it.

- Author(s)
- Published at
- Updated at
Milestones
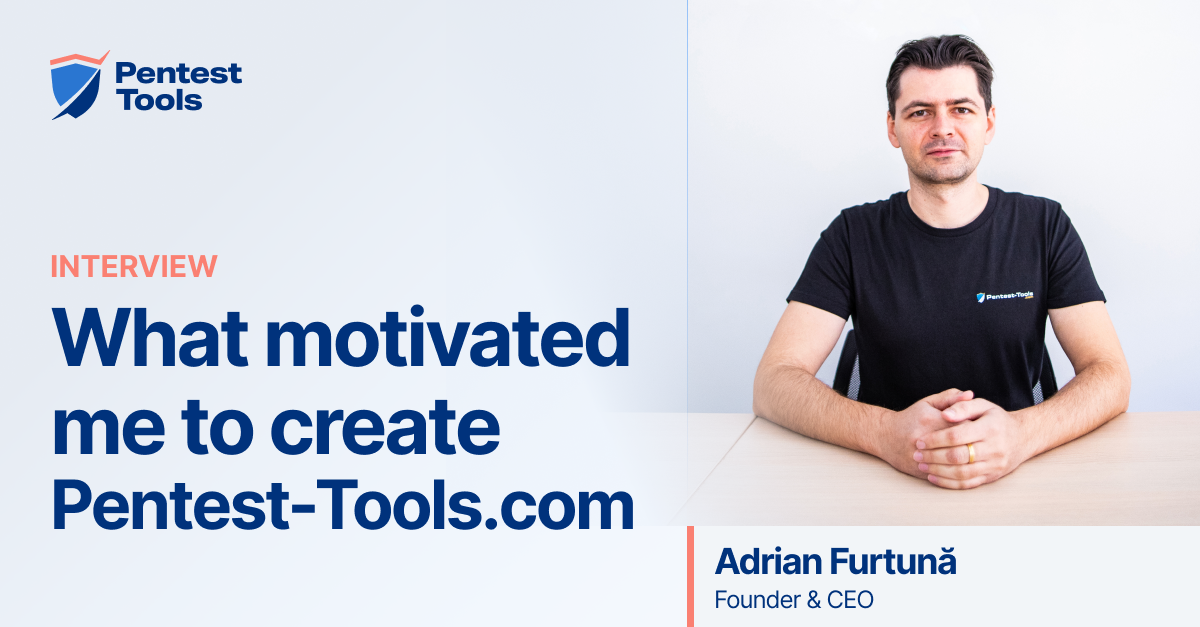
Behind the scenes – an interview with Adrian Furtuna, our founder and CEO
As cybercrime continues to escalate, businesses are increasingly prioritizing their cybersecurity strategies, often embracing penetration testing to address the most burning threats. Although this established practice is highly effective, there are still many necessary improvements to help scale it to the current needs of the tech ecosystem. CyberNews sat down with Adrian Furtuna, our Founder & CEO, to talk about the ins and outs of penetration testing. Here’s why Adrian believes that no matter how advanced the technology is, some aspects still need a human approach.
- Author(s)
- Published at
- Updated at
Security research
How to detect and exploit the Oracle WebLogic RCE (CVE-2020-14882 & CVE-2020-14883)
Pentesters love a good RCE, but, as much as we enjoy the thrill of detecting and exploiting it (ethically, of course), the tech ecosystem suffers every time one of these pops up. That’s why fast and effective recon and vulnerability assessment remain the go-to pentesting stages that help companies manage their risks so they can keep doing business and serving their customers. With your knowledge, experience, and advice, they can turn a potential hazard into a process that makes them stronger. Let’s take a closer look at the critical RCE vulnerability discovered in Oracle WebLogic Server and see how you can have a bigger positive impact in your organization and beyond it.
- Author(s)
- Published at
- Updated at

Security research
How to detect the Zoho ManageEngine ADSelfService Plus RCE (CVE-2021-40539)
Overwhelmed by so many high-risk vulnerabilities that emerge? Thousands of them are disclosed every year and 2021 is no exception. Systems are complex, cyber attacks get more sophisticated, and patching is still a challenge for many organizations. As infosec pros, it’s our responsibility to help companies (and individuals) understand the real implications and impact of a critical vulnerability and help them find it before it gets worse.
- Author(s)
- Published at
- Updated at
Security research
Detect and exploit Gitlab CE/EE RCE with Pentest-Tools.com (CVE-2021-22205)
“Just patch it!” is the usual advice when a vulnerability hits (and it’s not a zero-day). But it’s never that simple in organizations that have to manage layers upon layers of infrastructure. When you have to deal with a critical CVE like the latest unauthenticated RCE in Gitlab (CVSSv3 10.0), the tangled, messy process of patching bubbles to the surface.
- Author(s)
- Published at
- Updated at

Hacking tutorials
How to detect CVE-2021-22986 RCE with Pentest-Tools.com
As a pentester, when you see a major critical vulnerability persist for months in unpatched systems (like Log4Shell), you have a responsibility to help others understand its severity and how they can fix it. This is exactly why this article exists.

- Author(s)
- Published at
- Updated at
