
Security insights from the practitioners who validate and prioritize vulnerabilities
See how your team compares to the industry and bring real numbers to your next budget conversation. Every survey comes with a documented methodology, so you can check it yourself.
Our latest insights
Every survey we publish, on whatever topic, most recent first.
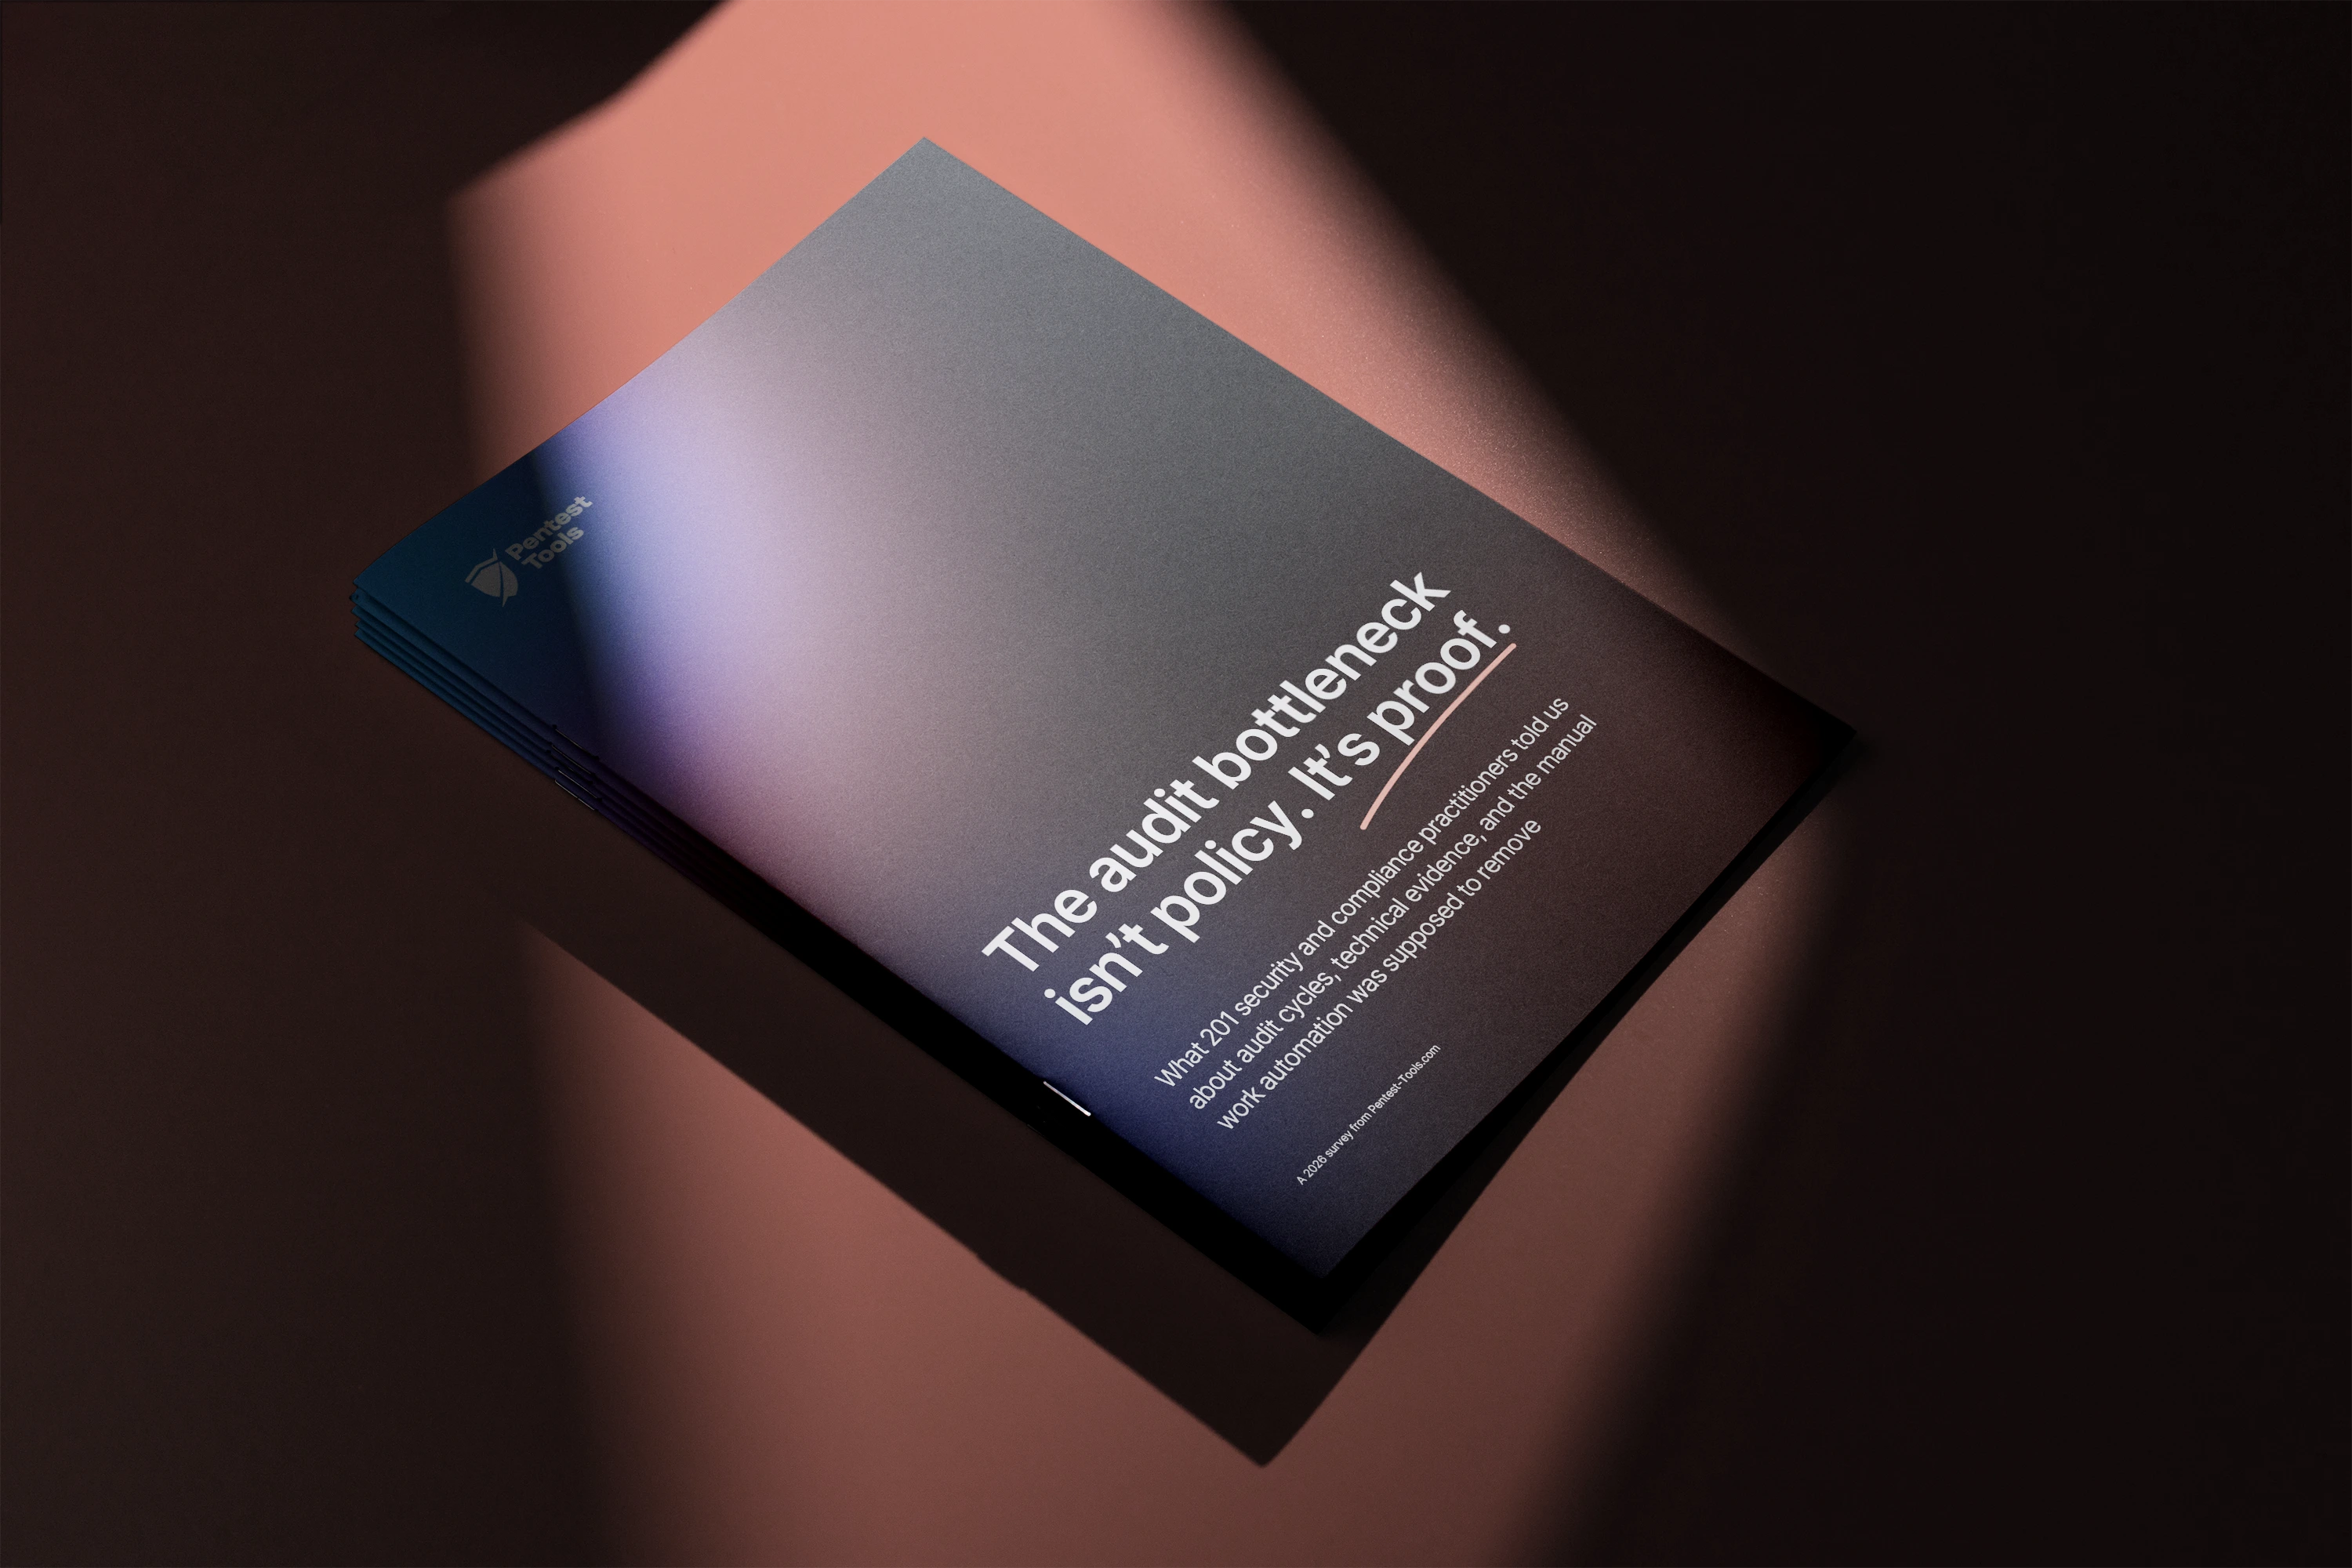
The audit bottleneck isn't policy. It's proof
Audit prep is where the evidence work actually piles up, according to 201 security and compliance practitioners.
→ 89.1% manually map or re-document evidence across compliance frameworks
→ 50.7% say getting time and input from technical teams is the biggest audit preparation bottleneck
AI pentesting in 2026: why testing cadence decides who copes
We surveyed 158 security practitioners about how AI is reshaping penetration testing and vulnerability discovery, and why validation is now the skill that separates teams which keep up from teams that get buried.
→ 88% of practitioners run into results that need significant manual validation
→ 63% rank false positive rate above cost when evaluating AI pentesting software
The shape of vulnerabilities to come: more subtle, context-dependent errors
If your team ships AI-assisted code, here's how - and when and where - security gaps that impact businesses emerge, according to 241 developers.
→ 20% find vulnerabilities in AI-assisted code post-deployment, always or often
→ Only 9% say vulnerability testing keeps pace with development
Why we publish these insights
We believe practitioner experience is evidence on its own, not just an opinion. This is our way of making that evidence accessible to everyone who shares the same challenges: security practitioners, internal teams, MSPs and MSSPs, and decision-makers who need actual data to act with confidence.
Responses directly from practitioners
The full dataset behind every stat we quote
What's changing in practice, not in theory
A new survey published the moment its data is ready
What you'll find here
From the raw data to how we collected it, here's what's inside.

Surveys
Real stats, unedited practitioner quotes, and the context behind each number.

Methodology
Exactly who we surveyed and how, so you have rich context for evaluating the data.
Where the data leads
The insights above point to a gap between finding a security issue and proving it’s exploitable.
Here's how Pentest-Tools.com closes it.
Compliance evidence
How validated findings become evidence auditors accept.
Proven accuracy
How Pentest-Tools.com validates findings instead of just flagging them.
Vulnerability research
How our own offensive security research team finds and discloses vulnerabilities before attackers do.
Real case studies
How other security and IT teams connect these insights - and Pentest-Tools.com - to their daily workflows and practice.
Trusted by 2,000+ security teams in 119+ countries
From internal security teams to global MSPs, security practitioners rely on Pentest-Tools.com for actionable insights that shape their workflows.


Keep unpacking
The gap between finding a vulnerability and proving it can impact the business doesn't have to be a problem. Compare plans and see how Confirmed findings close it.