
Vulnerability monitoring: continuous scans, precision alerts
Stop chasing noise. Track your attack surface with precision - scheduled scans, smart diff alerts, and zero distractions. You’ll only hear from us when it matters.
With Pentest-Tools.com’s vulnerability scanning tools, your team gets continuous visibility across web apps, networks, API, and cloud assets with minimal manual work.
Automation handles the scanning; security engineers decide what to do next.
How vulnerability scanning can create friction and risk
Scrambling when new CVEs drop slows everything down
Manual ad-hoc scans and asset chasing leave blind spots. Bulk scan scheduling and scan diffs sweep every asset and flag new exposures instantly.
Patching without proof wastes cycles
Don't rerun scans or wait for audits to confirm fixes. Scan diffs show “not detected” on the next run and build timestamped history for evidence.
Infrastructure changes quietly expand your attack surface
Deployments, configuration tweaks, or vendor updates can create vulnerable open ports or subdomains. Diff detection highlights them immediately, so exposures don’t linger.
Managing client scans manually eats into margins
MSPs and MSSPs waste hours juggling schedules and diffing results by hand. Workspaces and automated notifications keep cadence consistent.
Compliance cycles drain resources
Recurring assessments mean constantly searching for proof. Scheduled scans and diff reports align with cycles and generate audit-ready artifacts.
Vulnerability scanning that transforms your workflow

Set scans on autopilot
Set daily, weekly, monthly or custom scheduled scans, pick targets and recipients, then run them on autopilot. Results drop straight into inboxes or workflows. Trusted by hundreds of security teams, with over 2M scheduled scans run last year across web and network targets.

Bulk scanning that handles zero-day sweeps
Run scans across multiple targets at once when vulnerabilities drop. Bulk scheduling sweeps everything in parallel and highlights changes immediately.

Shared workspaces that keep teams and clients organized
Separate projects, clients, or departments into shareable workspaces. Keep the right level of access to each collaborator and schedules, alerts, and results scoped.

Scan diffs with clear guardrails
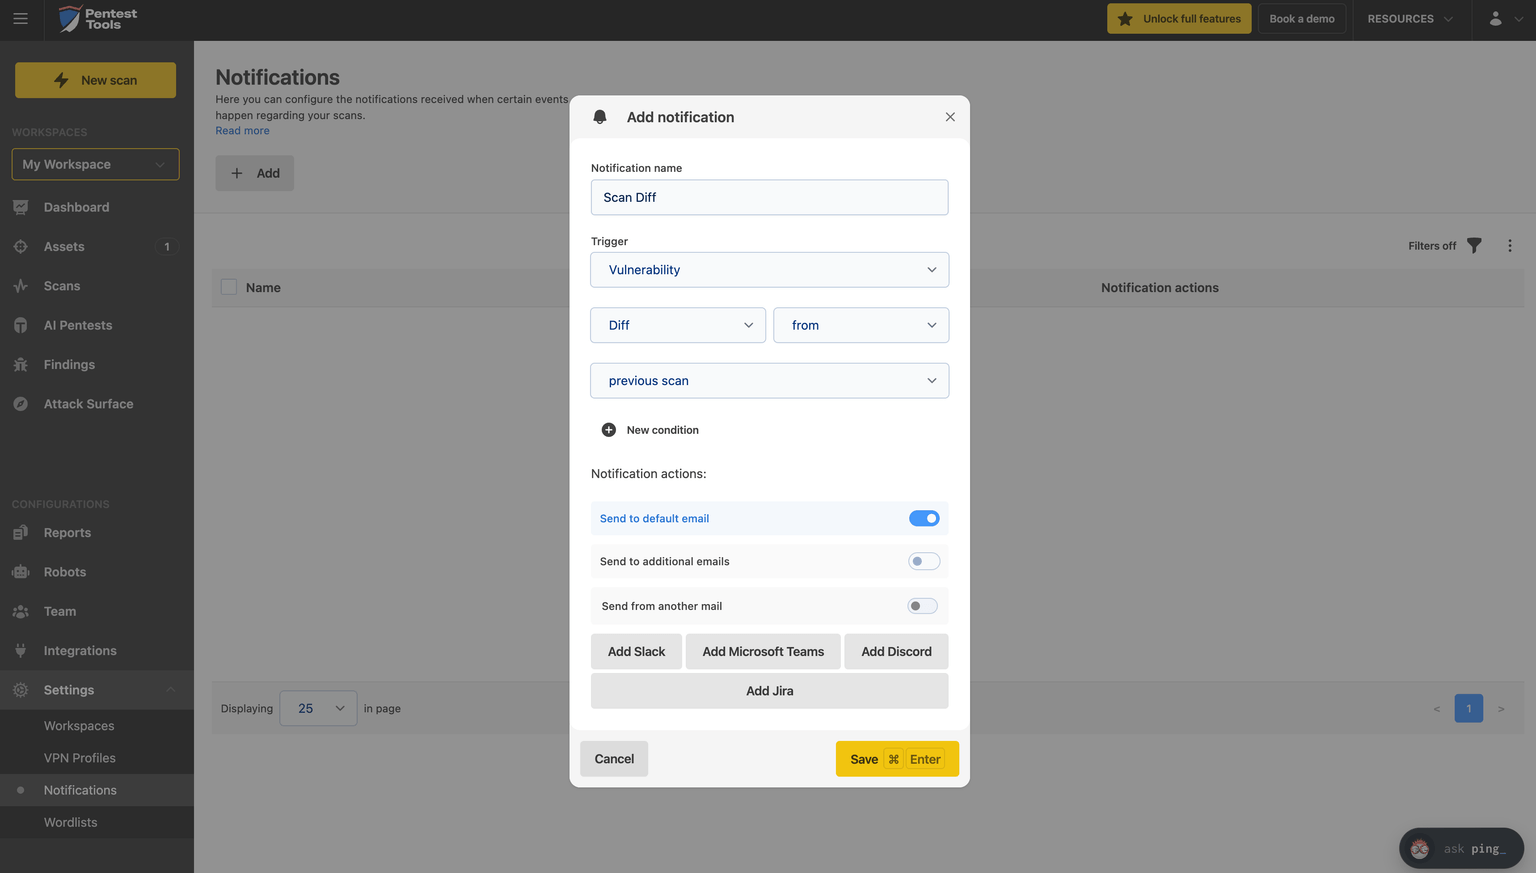
Compare the latest finished scan for the same target, workspace, and tool. Get alerts only for new, resolved, or updated findings – it’s never the same noise twice, so you only act on meaningful changes. Learn more about scan diffs. Note: Scan diff doesn’t yet consider parameter changes and only compares to the previous run. Keep track of patched issues versus those that reappear for other reasons.

Reporting that doesn’t make you work for evidence
Generate polished DOCX, PDF, or HTML reports instantly. Templates auto-fill with findings, summaries, and remediation advice ready for stakeholders and auditors – doing the repetitive part of the work for you.

Integrations that plug into your day-to-day workflow
Powerful integrations push alerts and results to Slack, Microsoft Teams, Discord, Jira, webhooks, or CI/CD pipelines. Trigger scans programmatically and keep everyone in sync. Email alerts are available on all plans; Teams, Slack, Discord, and webhooks on supported plans.

Scan Robots that automate follow-ups
Automate repeatable security testing with Scan Robots. Each robot passes relevant results from one tool to the next, so your team reviews the findings instead of launching each scan by hand.

A unified toolkit that covers web, network, and cloud
Proprietary scanners for web apps, APIs, networks, and cloud assets work together in one product, with new detections added daily. Results feed into scheduling, diff alerts, reporting, and automation. Where supported, Sniper safely exploits what the scanners find, so your team prioritizes on proven risk, not theoretical severity.
Streamline compliance, strengthen security, and improve collaboration
Our vulnerability scanning tools turn sweeps into outcomes. Respond faster, stay aligned, and have audit-ready proof of progress – whether you’re tracking a handful of assets or hundreds.
Continuous visibility without busywork
Automate recurring scans and focus only on meaningful changes.
Faster response to risks
See new exposures right away through diff alerts, not by parsing old reports.
Improved team coordination
Push notifications to Teams, Slack, or Shared Workspaces so everyone stays aligned.
Audit-ready evidence
Maintain a clear history of detected, updated, and resolved findings. Timestamped scan diffs support PCI DSS, ISO 27001, SOC 2, and other recurring requirements.
Customized monitoring
Set frequency and time zone, choose recipients, and filter emails by condition.
Flexible at scale
Monitor a few critical targets or hundreds of assets across clients and departments.
See vulnerability monitoring catch what changed, step by step
See how to put scans on a schedule and get alerts only when something changes. Follow the setup step by step, then repeat it on your own targets.
How security teams can put vulnerability monitoring to work
Sweep for zero-days on release
Run bulk scans across your environment as soon as new CVEs drop. Scan diffs show exactly what changed, so you know which assets need attention first.
Validate remediations fast
Confirm patches without waiting for audits. The next scheduled run shows issues as “not detected” with timestamped proof for stakeholders.
Detect drift after infrastructure changes
Stay on top of an evolving attack surface. Scheduled scans catch new open ports, services, or subdomains introduced by configuration changes or deployments.
Monitor many clients with ease
MSPs and MSSPs can isolate clients in workspaces with per-client schedules. Automated diff notifications cut out manual comparisons and reduce errors.
Stay aligned with compliance cycles
Schedule scans to match PCI DSS, ISO 27001, or other recurring frameworks. Diff reports provide ongoing evidence without the reporting grind.
Start monitoring what changed – not what didn’t
Run scheduled scans across web, network, and cloud assets. Only receive alerts that matter. Transform your vulnerability monitoring capability.
Vulnerability Monitoring FAQs
What triggers a scan diff notification?
You get an alert when the latest finished scan for the same target, workspace, and tool shows new, updated, or resolved findings compared to the previous run.
How often can I schedule scans?
You can schedule scans daily, weekly, monthly or customized to fit your workflows. You can also launch ad-hoc scans whenever you need.
Which channels can I receive notifications on?
Email on all plans. Microsoft Teams, Slack, Discord, and webhooks are available on supported plans.
Which tools support scan diff?
Scan diff works with many of our tools, including Website Scanner, Network Scanner, Subdomain Finder, and Port Scanner. It compares each run with the previous one, so recurring scans surface what’s new and what changed.
Does scan diff consider changes in scan parameters?
Not yet. Diffs compare results only, using the previous run as the baseline.
How does monitoring help with compliance requirements?
Scheduled scans and diff history align with PCI DSS, ISO 27001, SOC 2, and other recurring frameworks. Reporting exports give you ready-made DOCX, PDF, or HTML evidence.
Can I monitor multiple clients or departments?
Yes. Use shared workspaces to isolate projects or clients, apply per-client schedules, and route notifications to the right channels.