Changelog

These are the latest updates we've made to our platform. If you have any questions about any of the updates you see below, please feel free to contact us!

Date

June 2026

  1. Jira integration: credentials are checked before saving

    Copy link to “Jira integration: credentials are checked before saving”

    Jira integrations now test your credentials before saving them, so a typo gets caught up front instead of the first time you try to push a finding.

    A wrong token or a mistyped host used to sit quietly until a push failed mid-workflow. Now the integration briefly validates what you entered and tells you immediately if it won’t work, which cuts out a common source of broken integrations and support tickets.
April 2026

  1. Filter /findings output by risk level via API

    Copy link to “Filter /findings output by risk level via API”

    The /findings endpoint now accepts min-risk-level and max-risk-level parameters. Use either or both:

    • min-risk-level: returns findings at or above the specified level (e.g. high and critical only)

    • max-risk-level: returns findings at or below the specified level (e.g. medium and below)

    • Combine both to retrieve a specific range (e.g. medium only)

    Automation pipelines no longer need to pull everything and filter client-side. Payload size drops for integrations feeding SIEMs, ticketing systems, or reporting tools. Pairs with existing /findings filters for more precise data retrieval.

    Read the API docs

August 2025

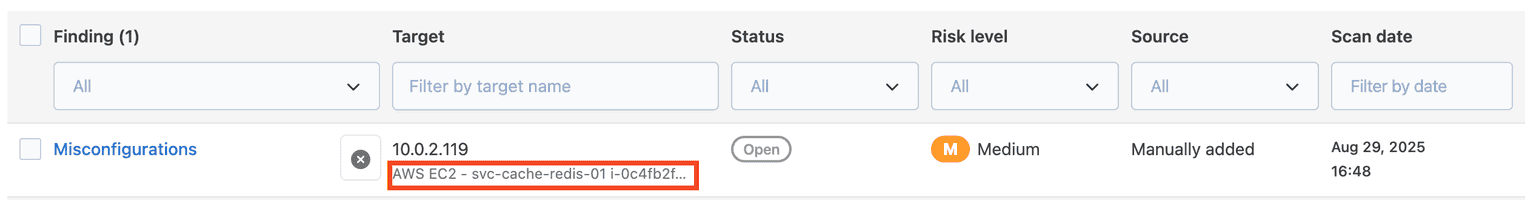
  1. We’ve added even more improvements that make asset and findings management more efficient:

    Multiple AWS regions – Import assets across multiple regions (default region config) without adding separate integrations.

    Asset descriptions everywhere – Asset descriptions now show in Scans and Findings (including manual findings) for easier identification.

October 2024

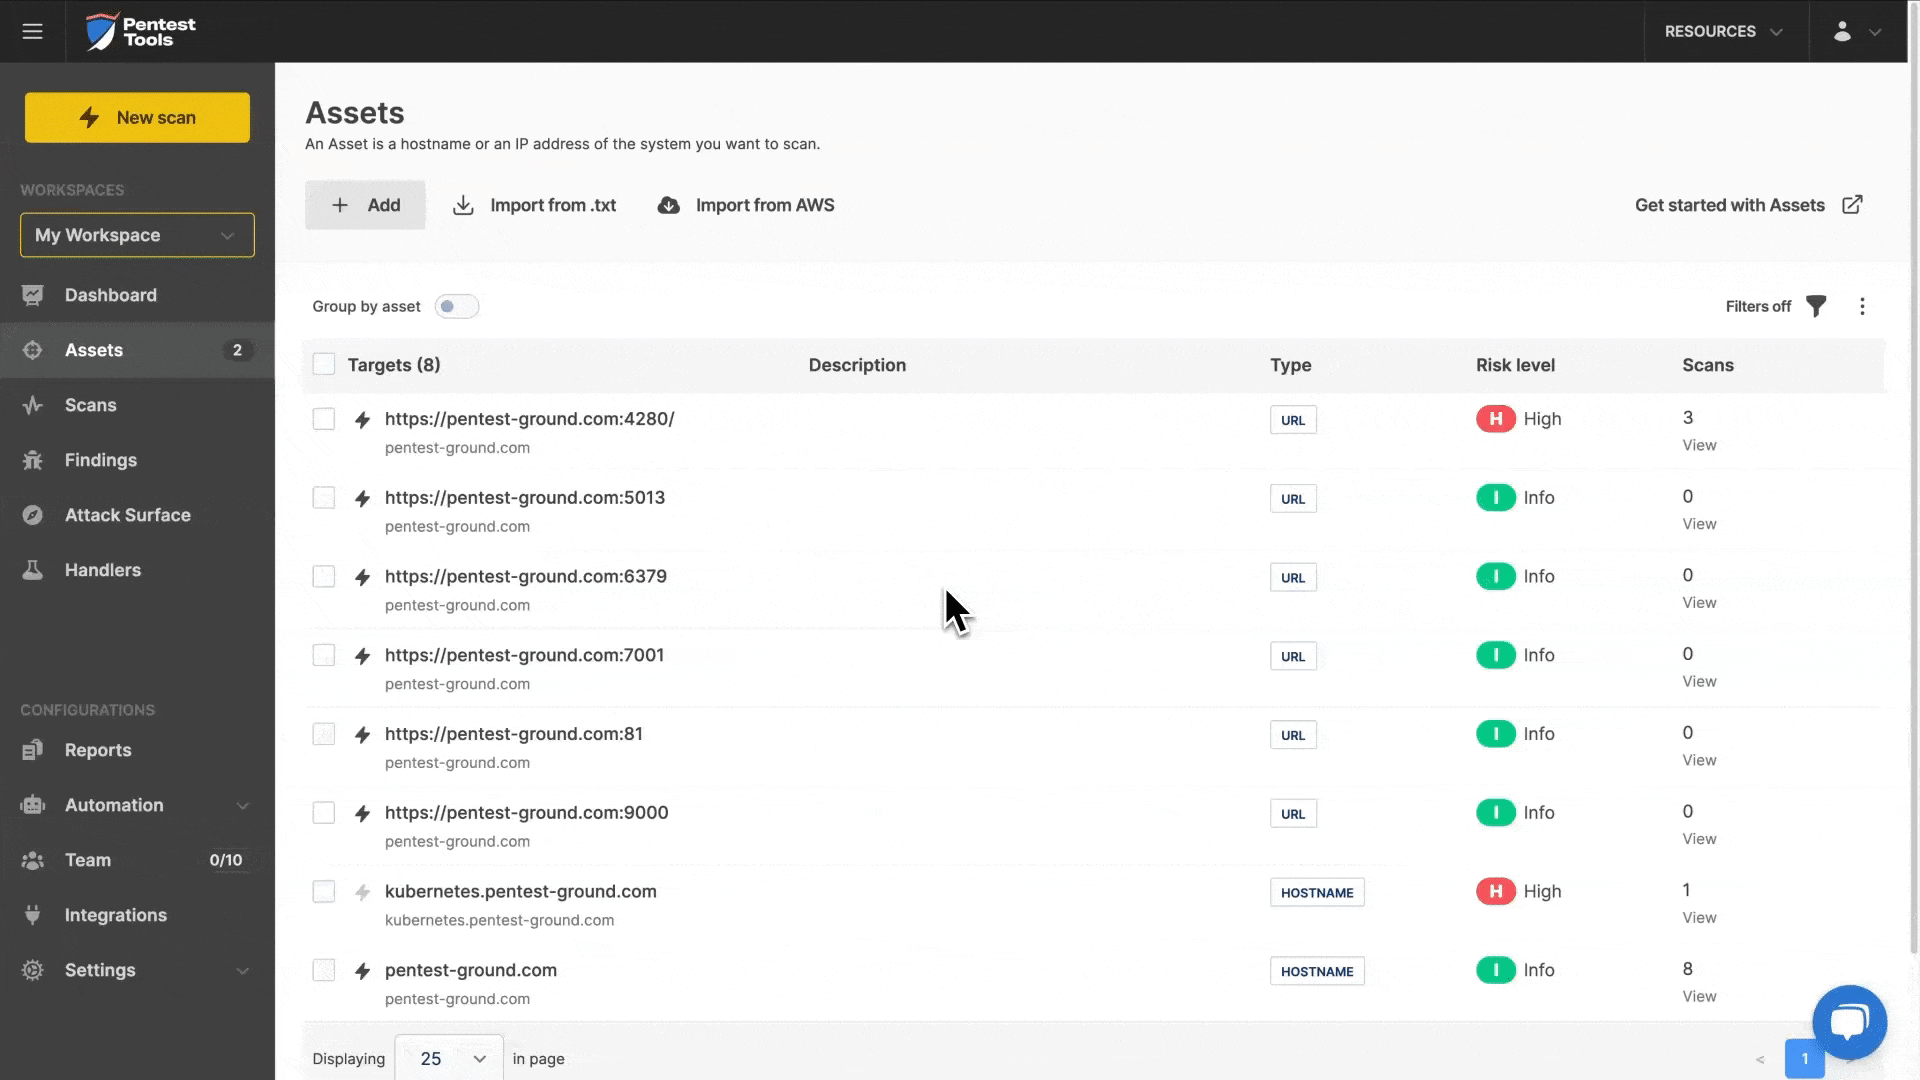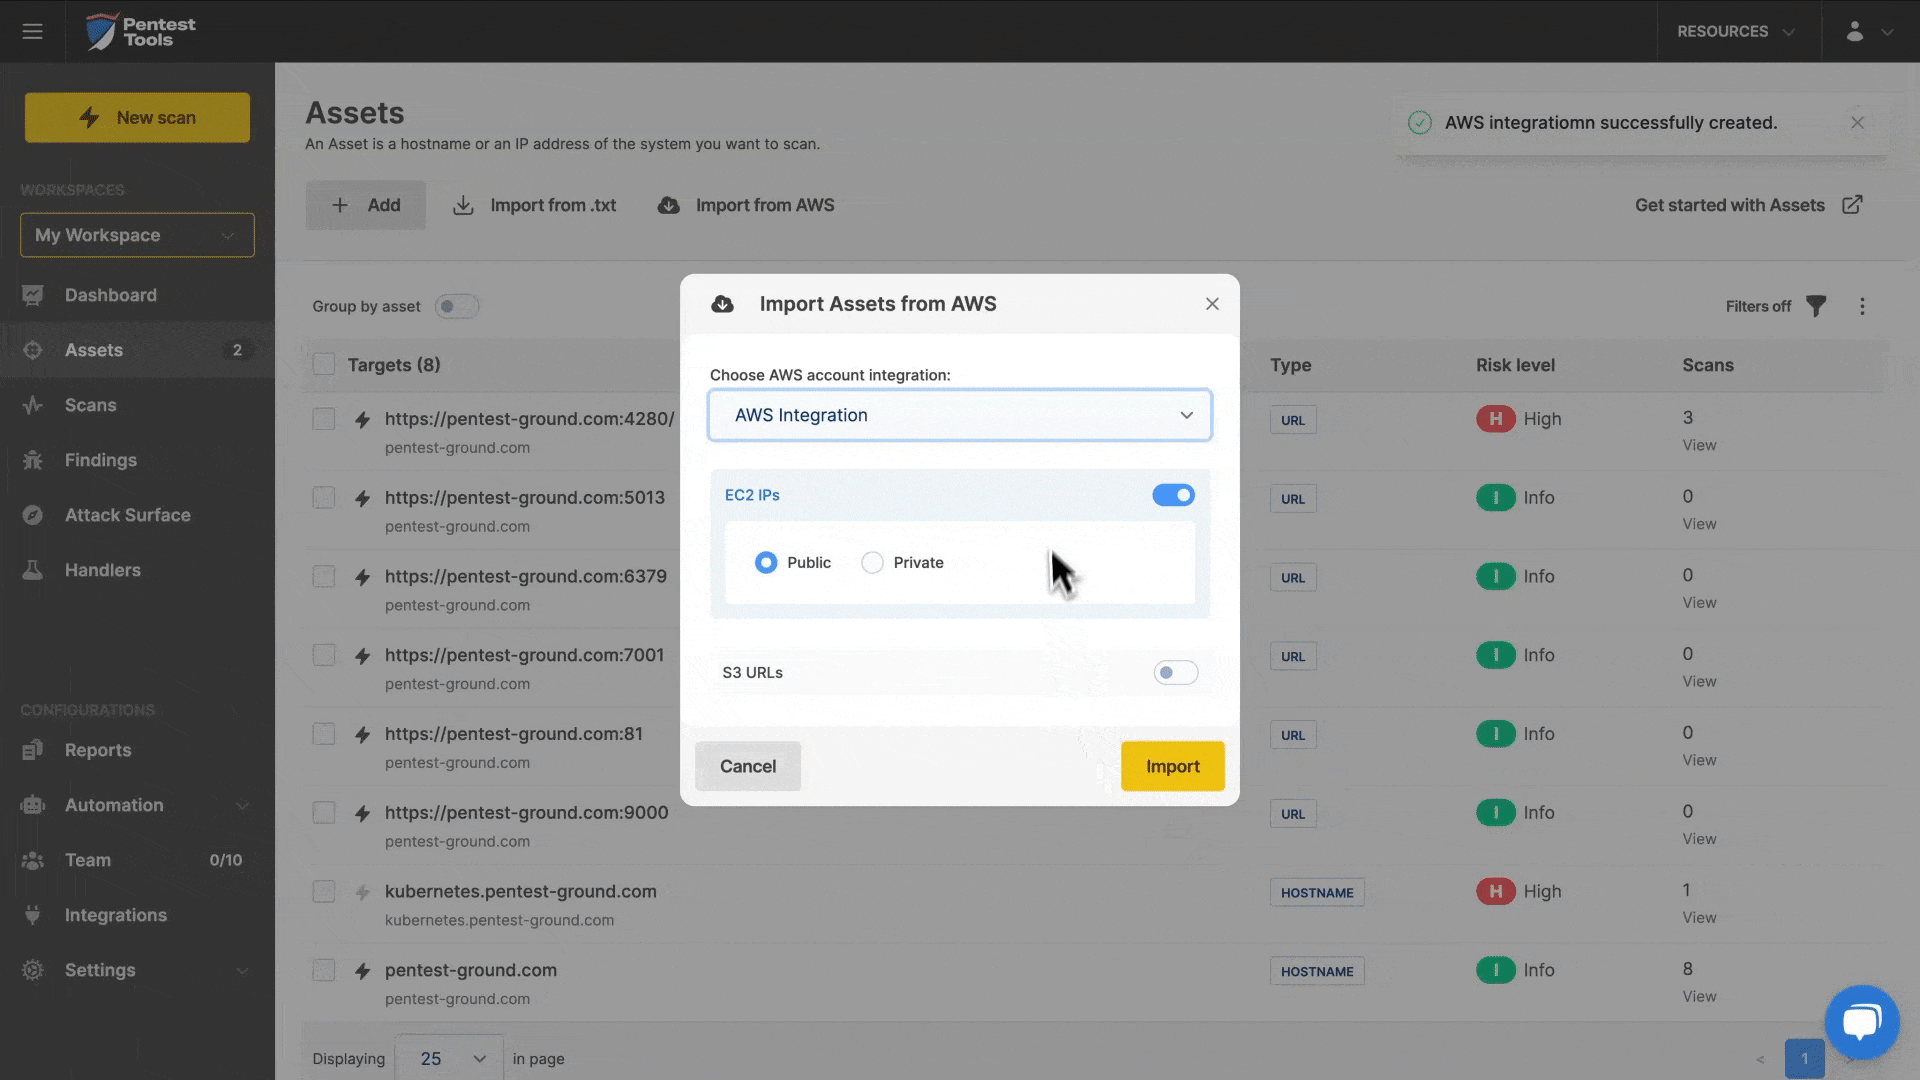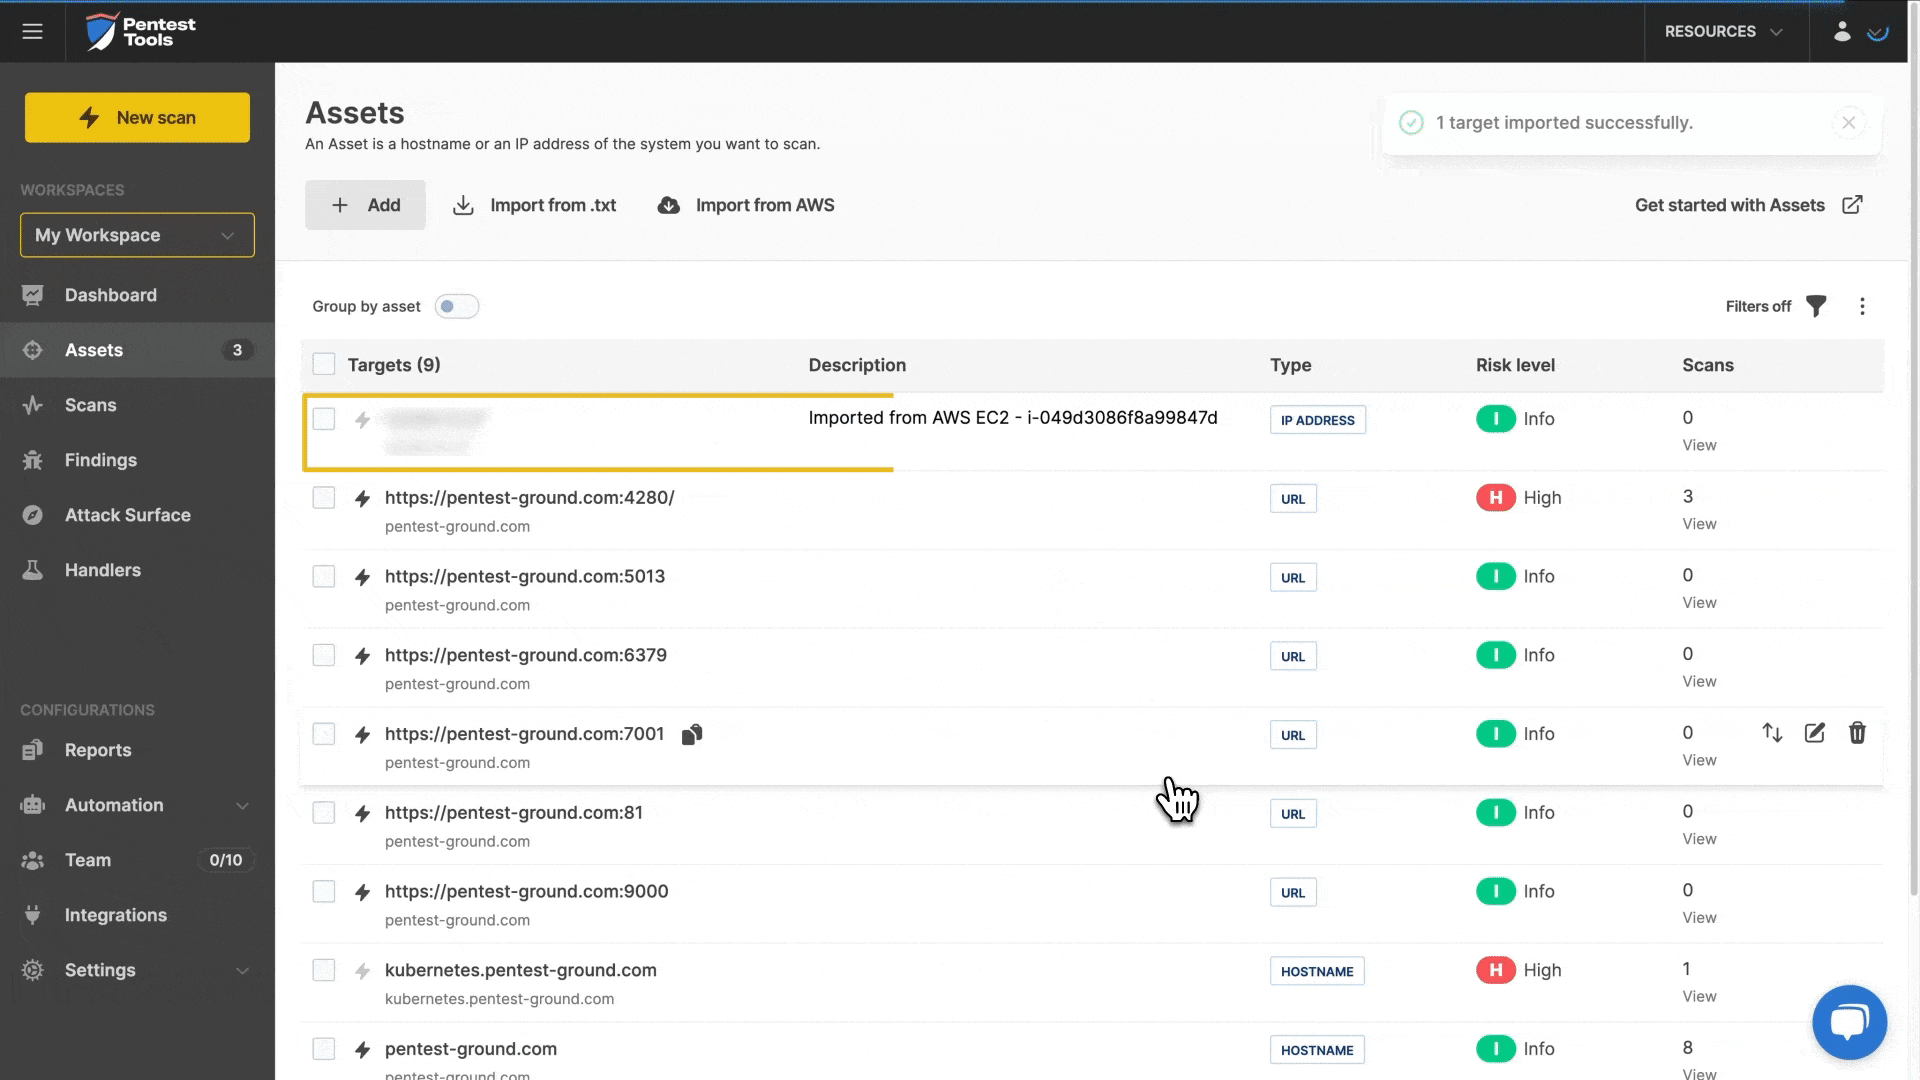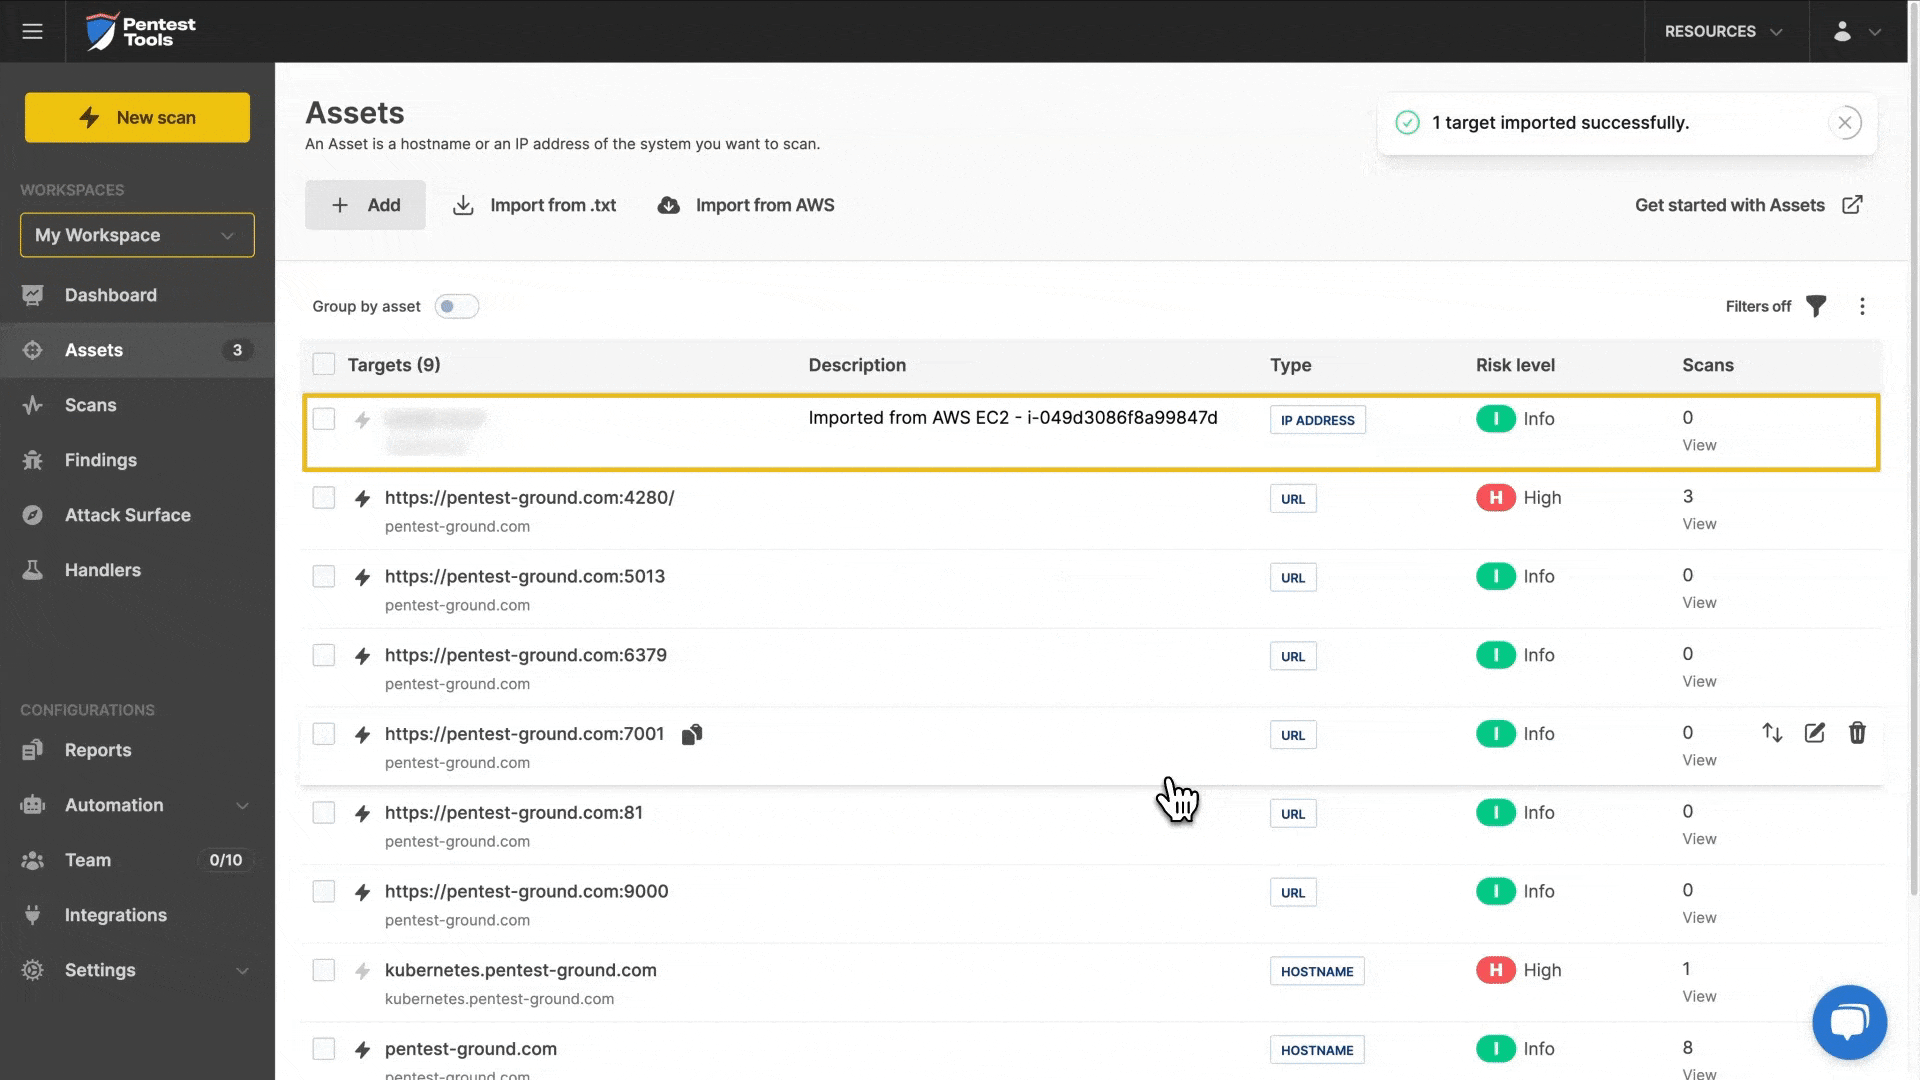
  1. NEW: Import your AWS targets with ease

    Copy link to “NEW: Import your AWS targets with ease”

    There’s a new cloud integration in your Pentest-Tools.com toolkit!

    Now you can easily import AWS targets to your account with a fast setup.

    We’re constantly expanding our integrations to improve your pentesting workflow experience. If you have any preferred tool we should consider next, let us know!

July 2024

  1. Even more integrations for more focused security workflows

    Copy link to “Even more integrations for more focused security workflows”

    Are you on the lookout for more efficiency in your workflows? (Who isn't, right?)

    We've got a growing list of integrations so you run your security operations smoothly.

    Just added:

    • Discord - a popular request in our community! Get custom notifications for scan results, set different channels for specific alerts, and make sure everyone sees the relevant findings.

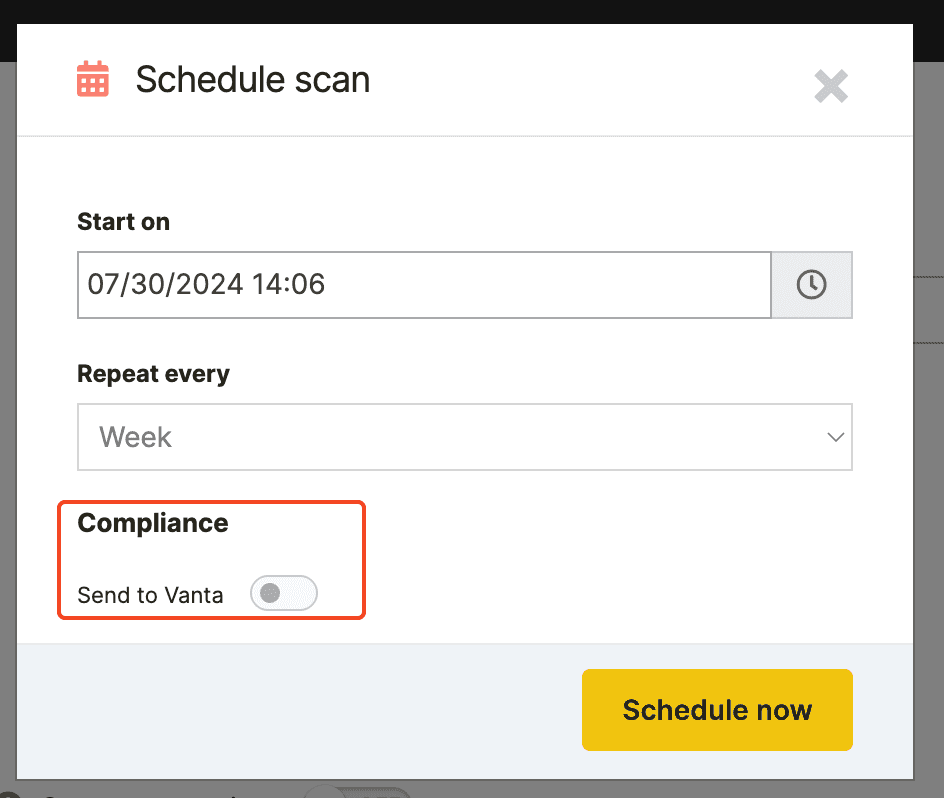
    • Vanta - another popular request! Use it to automatically get PDF reports from scheduled scans only straight to your Vanta account and make compliance operations a bit smoother.

    • You can now use the CLI version for our Website Vulnerability Scanner to set up vulnerability tests in your CI/CD flow.

    Our colleague Mihai explains how to use it in this quick video:

    Use automated GitHub Actions to test web app configurations & deployments for vulnerabilities

April 2024

  1. Zoom in and out on details across your projects

    Copy link to “Zoom in and out on details across your projects”

    3 improvements you’ll notice as you log into your account:

    • Single sign-on with Microsoft - jump straight into action using your existing Microsoft account

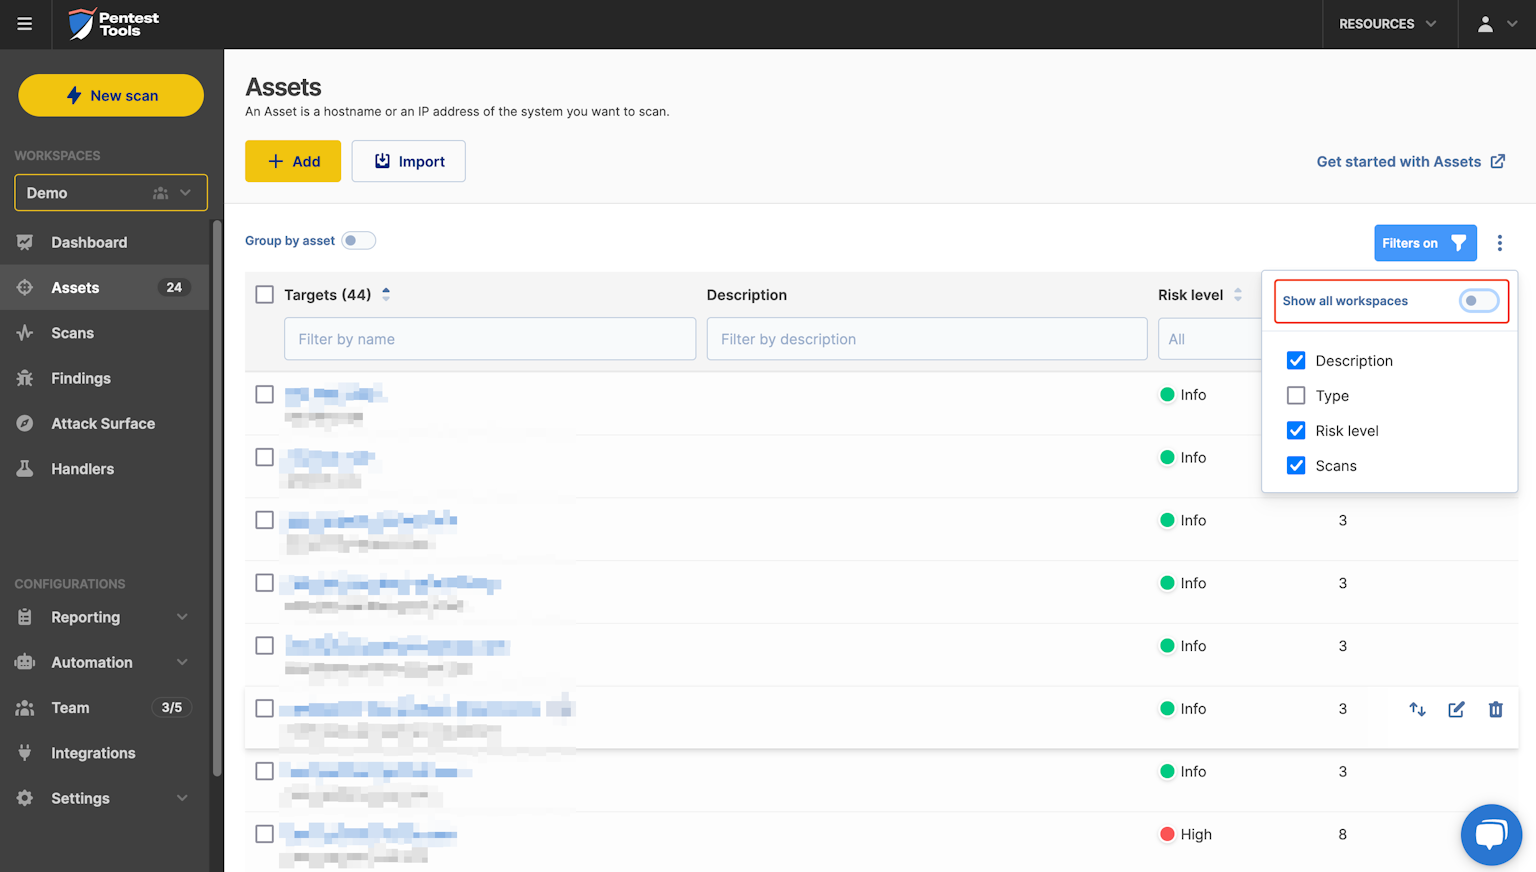
    • View all assets across workspaces - easily search for, identify, and manage duplicate assets from all your workspaces at once.

    view all assets

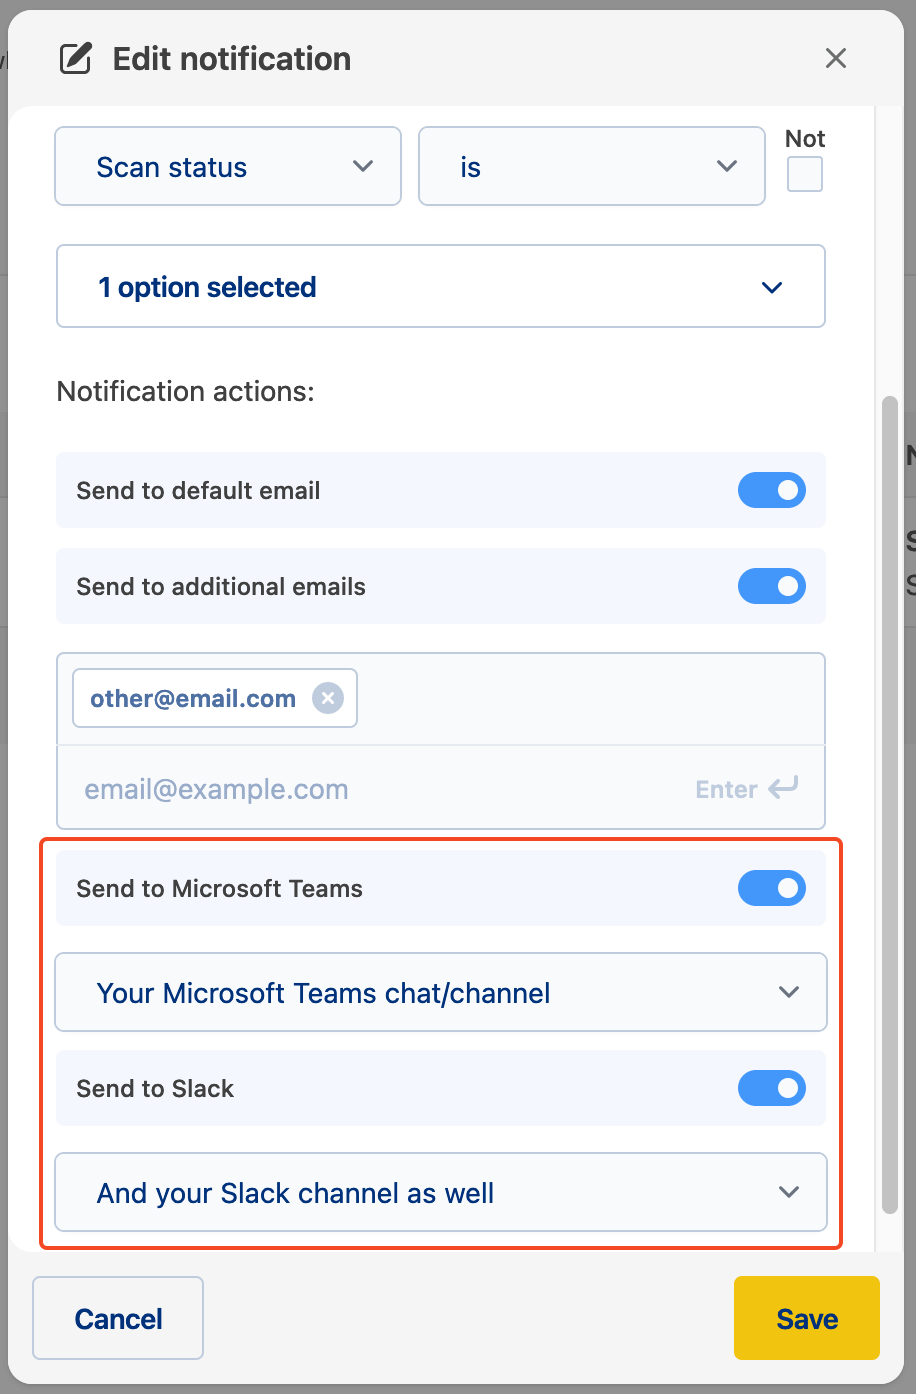
    • Unified notifications across integrations: you can now get the same notification through multiple services, in preparation for even more integration options we’ll launch in the future.

    multiple integrations