Changelog

These are the latest updates we've made to our platform. If you have any questions about any of the updates you see below, please feel free to contact us!

Date

May 2024

    • CVE-2024-24919 (CVSSv3 8.6) - can remote, unauthenticated attackers read the contents of any file on affected Check Point VPN servers, including password hashes for local accounts or SSH private keys?

    • CVE-2022-31137 (CVSSv3 9.8) - can ransomware actors gain remote access to Roxy Wi, the server management GUI, using this vulnerability?

    • CVE-2024-27198 (CVSSv3 9.8) - can attackers use this critical CVE to get RCE on your JetBrains TeamCity server?

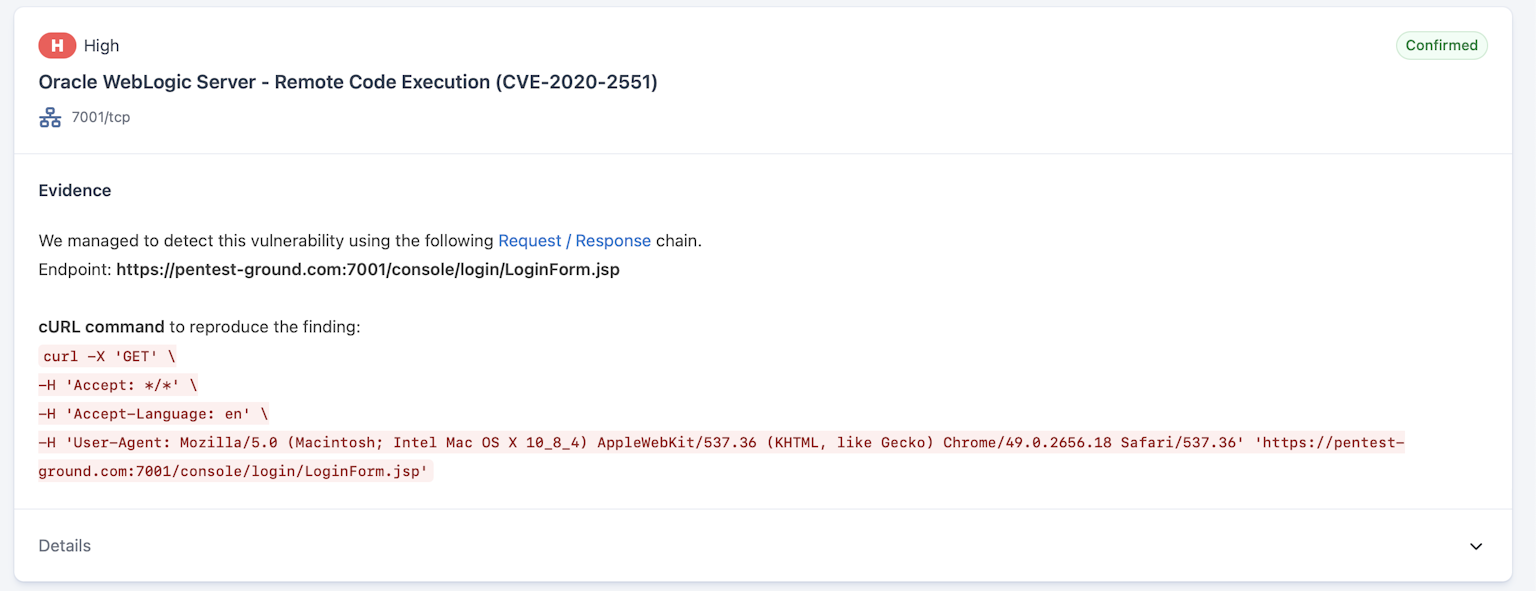
    These three custom exploitation modules our team added to Sniper will give you the answers - and proof! (The module for CVE-2024-24919 is coming in the next 48 hours).
  1. Finished and scheduled scans - in the same screen

    Copy link to “Finished and scheduled scans - in the same screen”

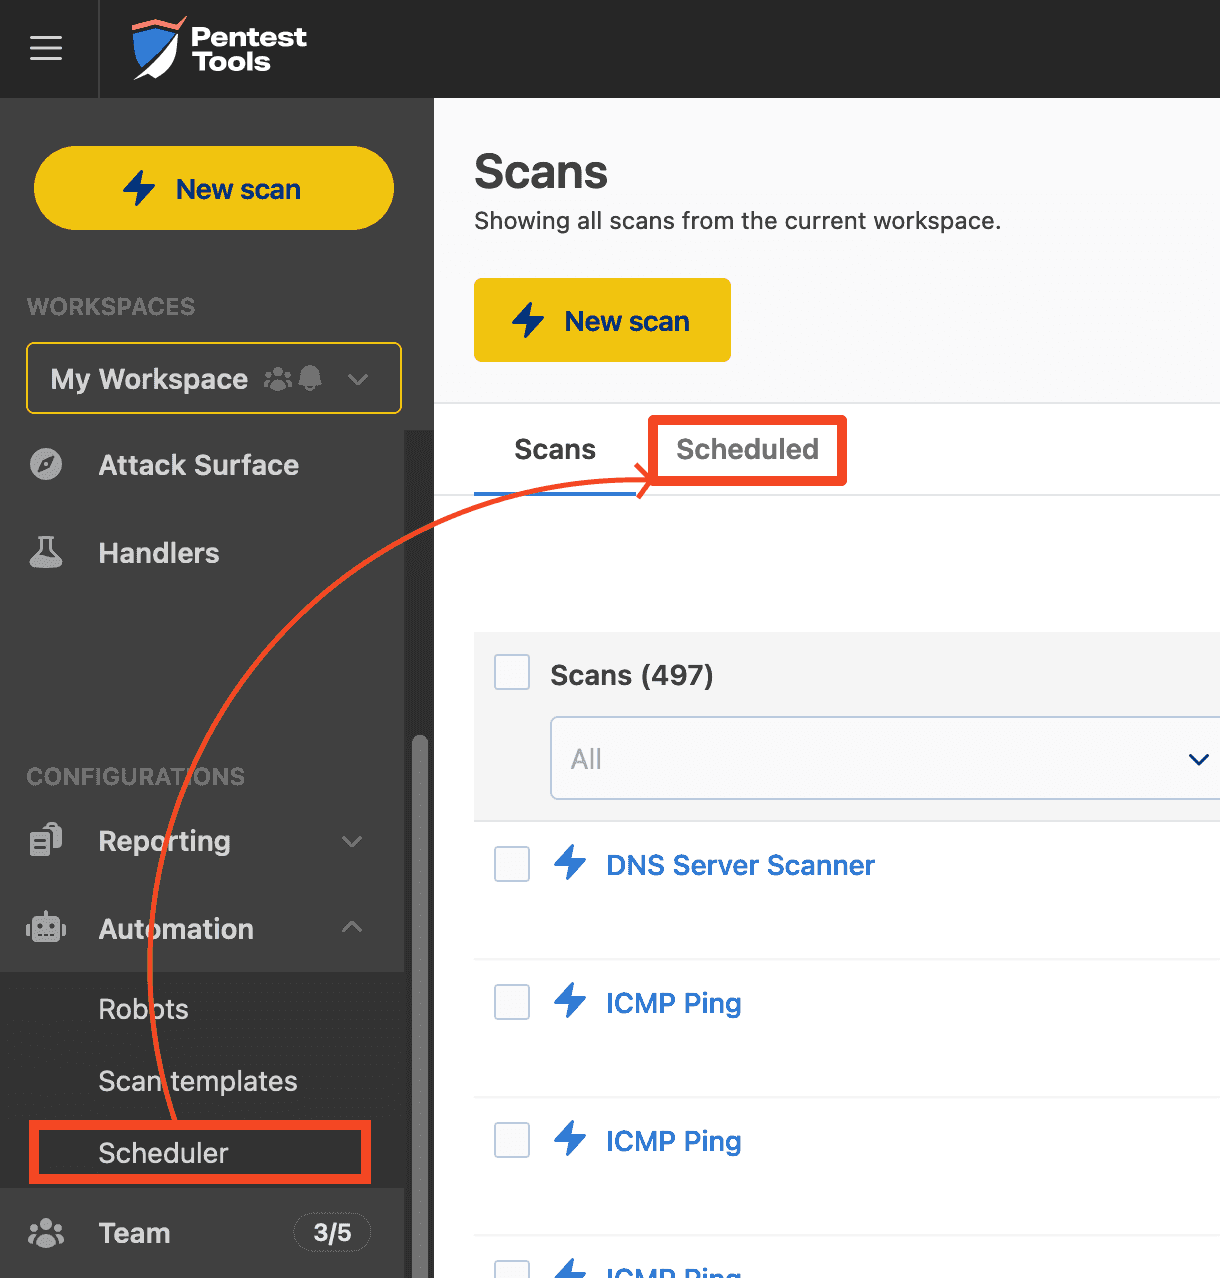
    Your scheduled scans now sit next to your finished scans (in separate tabs, don't worry).

    scheduled scans merged

    Moving scheduled scans from the Automation tab to Scans makes it easier to keep an eye on them and adjust them as your needs change.

April 2024

  1. Get far-reaching findings with the Network Scanner

    Copy link to “Get far-reaching findings with the Network Scanner”

    We've introduced crucial detections for security issues that expand your attack surface:

    • Publicly exposed VNC, MSSQL, and LDAP services - findings now flag if these services are publicly accessible on the Internet, so you can tighten your network's security posture

    • CVE-2023-3824 (CVSSv3 9.8) - stack buffer overflow in PHP that leads to RCE

    • CVE-2023-44487 (CVSSv3 7.5) - we enhanced detection accuracy for HTTP/2 Rapid Reset by checking if the target supports the HTTP/2 protocol and the HTTP/2 RST_STREAM directive

    • Comprehensive DNS records - see a new finding when a target has DNS records available (A, AAAA, MX, NS, SOA, TXT, SPF, CAA, CNAME) and get deeper visibility into the target’s domain structure.

  2. Confirm business risk with Sniper’s new precision strikes

    Copy link to “Confirm business risk with Sniper’s new precision strikes”

    Sniper just got sharper with new exploits for two critical CVEs:

    • CVE-2024-0204 (CVSSv3 9.8) - assess the business risk of the Authentication Bypass vulnerability in GoAnywhere MFT, which leads to RCE by uploading a webshell

    • CVE-2024-1212 (CVSSv3 10) - validate the threat of exploiting this Remote Code Execution vulnerability in Progress Kemp LoadMaster

  3. Leave no stone unturned with these Website Scanner upgrades

    Copy link to “Leave no stone unturned with these Website Scanner upgrades”

    Our Website Vulnerability Scanner now:

    • Detects flaws in JWT implementations by checking if web apps that use JWTs for authentication allow them to have a None or random signature, creating security risks

    • Runs faster light web app scans that also come with detailed requests and responses for each finding

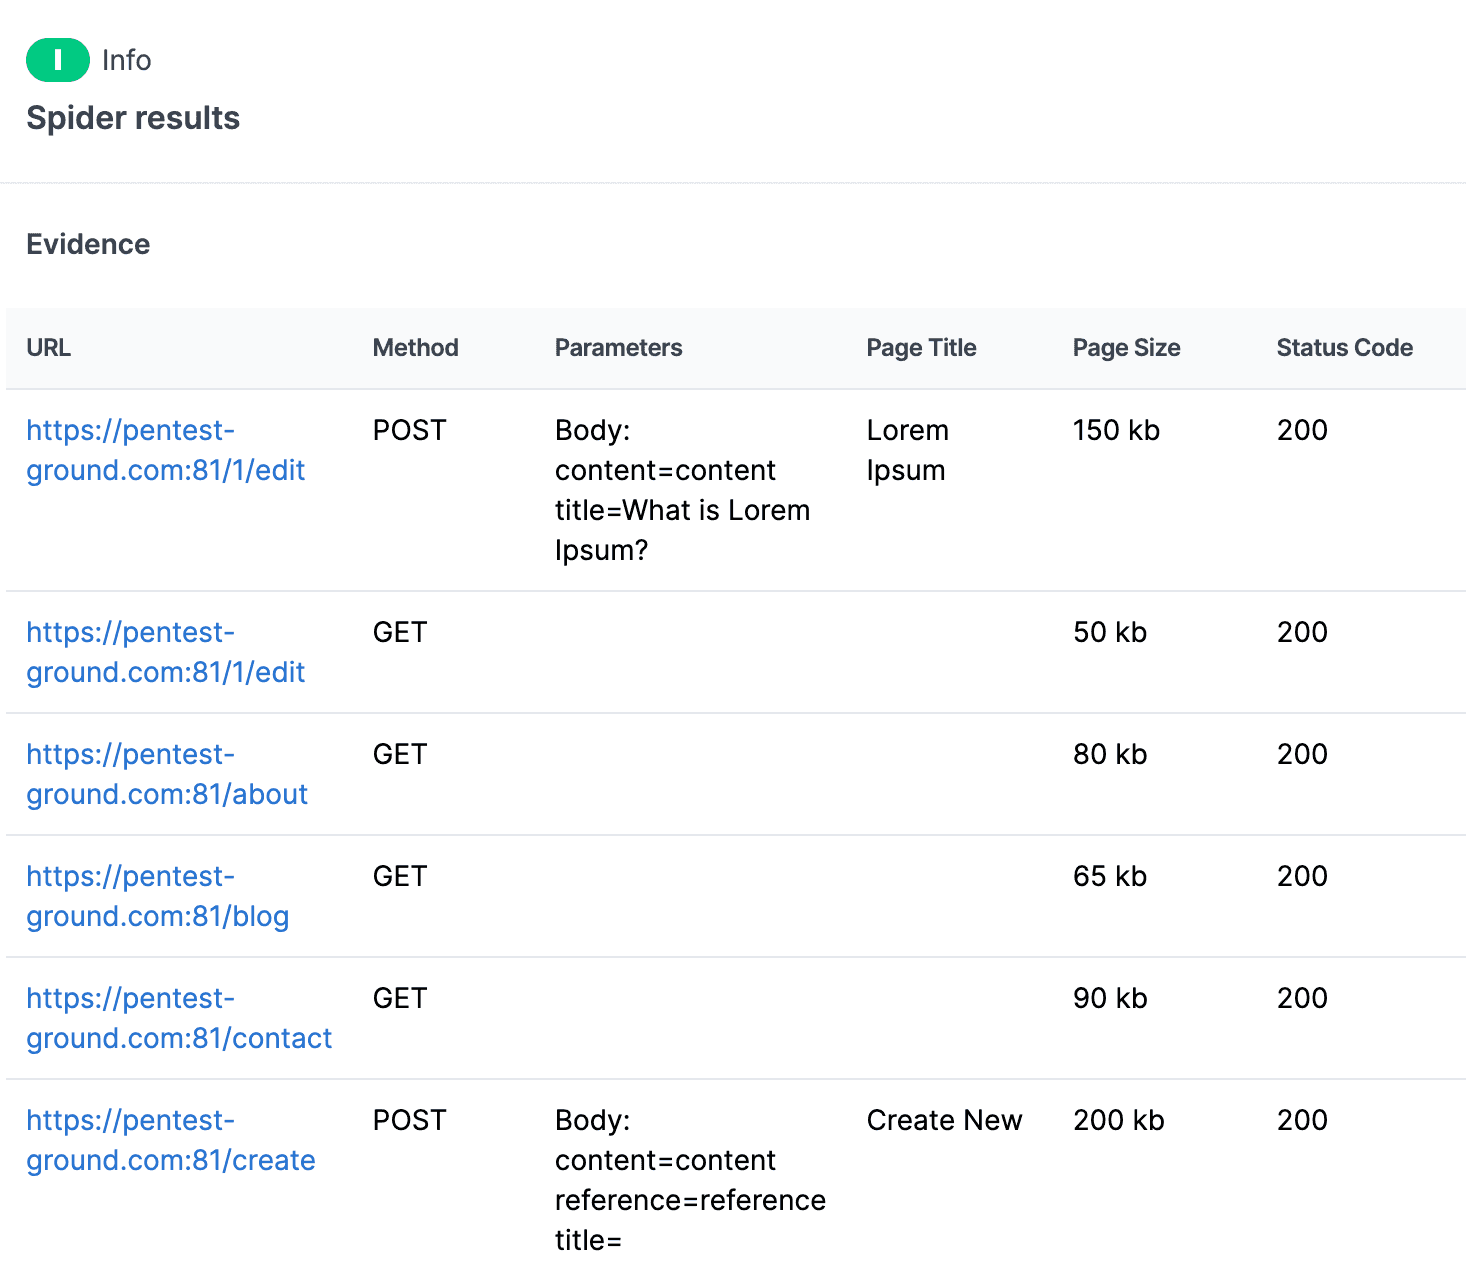
    • Provides extra information about spidered responses in evidence which now includes the status code, page title, and page size for each URL

    • Extracts proof of exploitation for Linux OS command injection in the form of hostnames and usernames.

  4. Zoom in and out on details across your projects

    Copy link to “Zoom in and out on details across your projects”

    3 improvements you’ll notice as you log into your account:

    • Single sign-on with Microsoft - jump straight into action using your existing Microsoft account

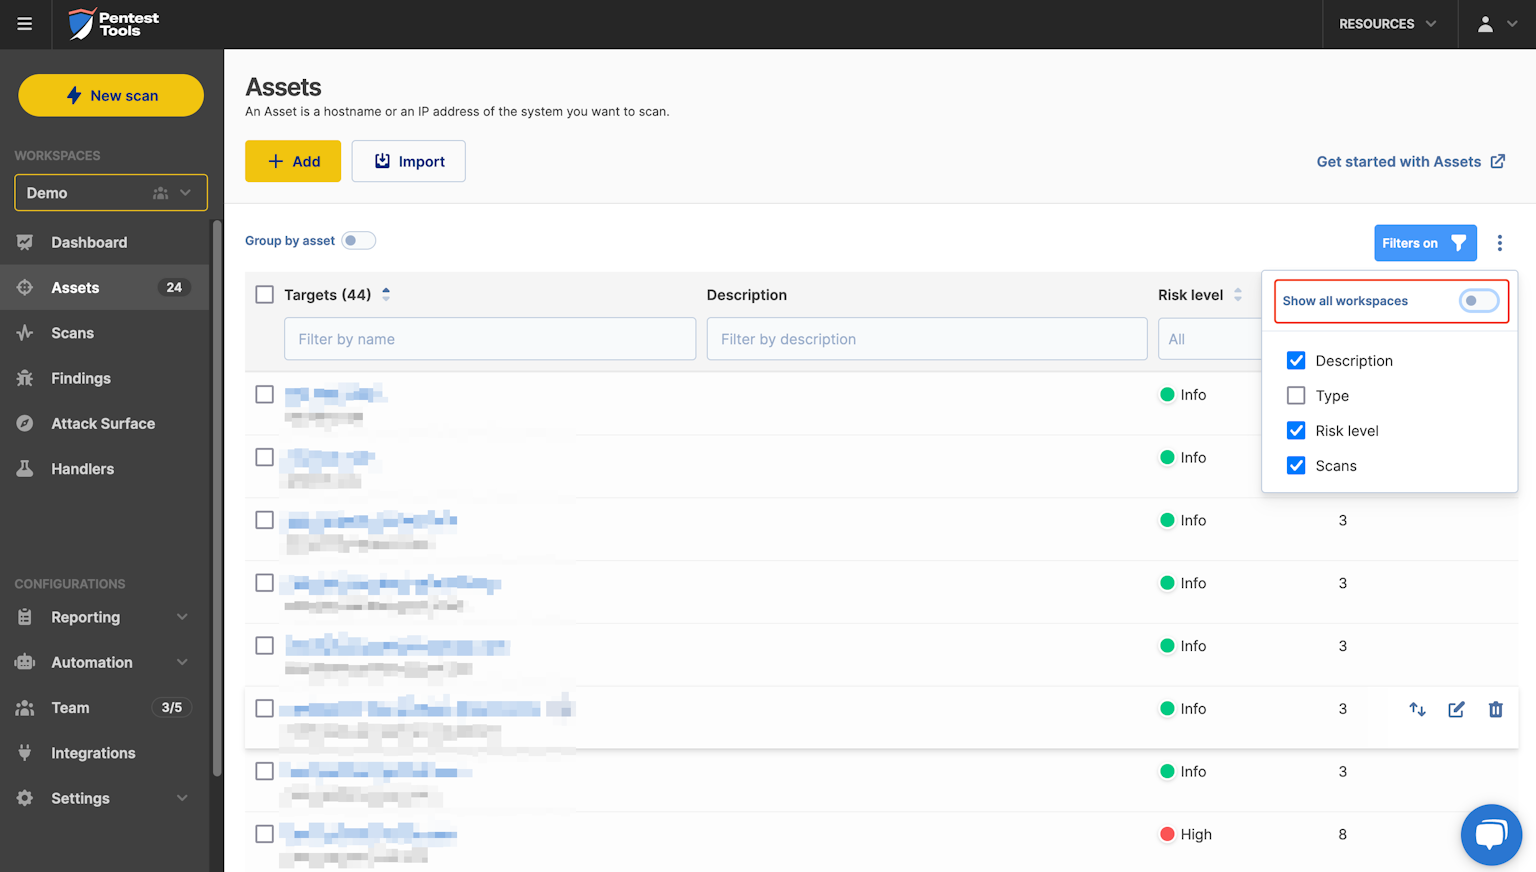
    • View all assets across workspaces - easily search for, identify, and manage duplicate assets from all your workspaces at once.

    view all assets

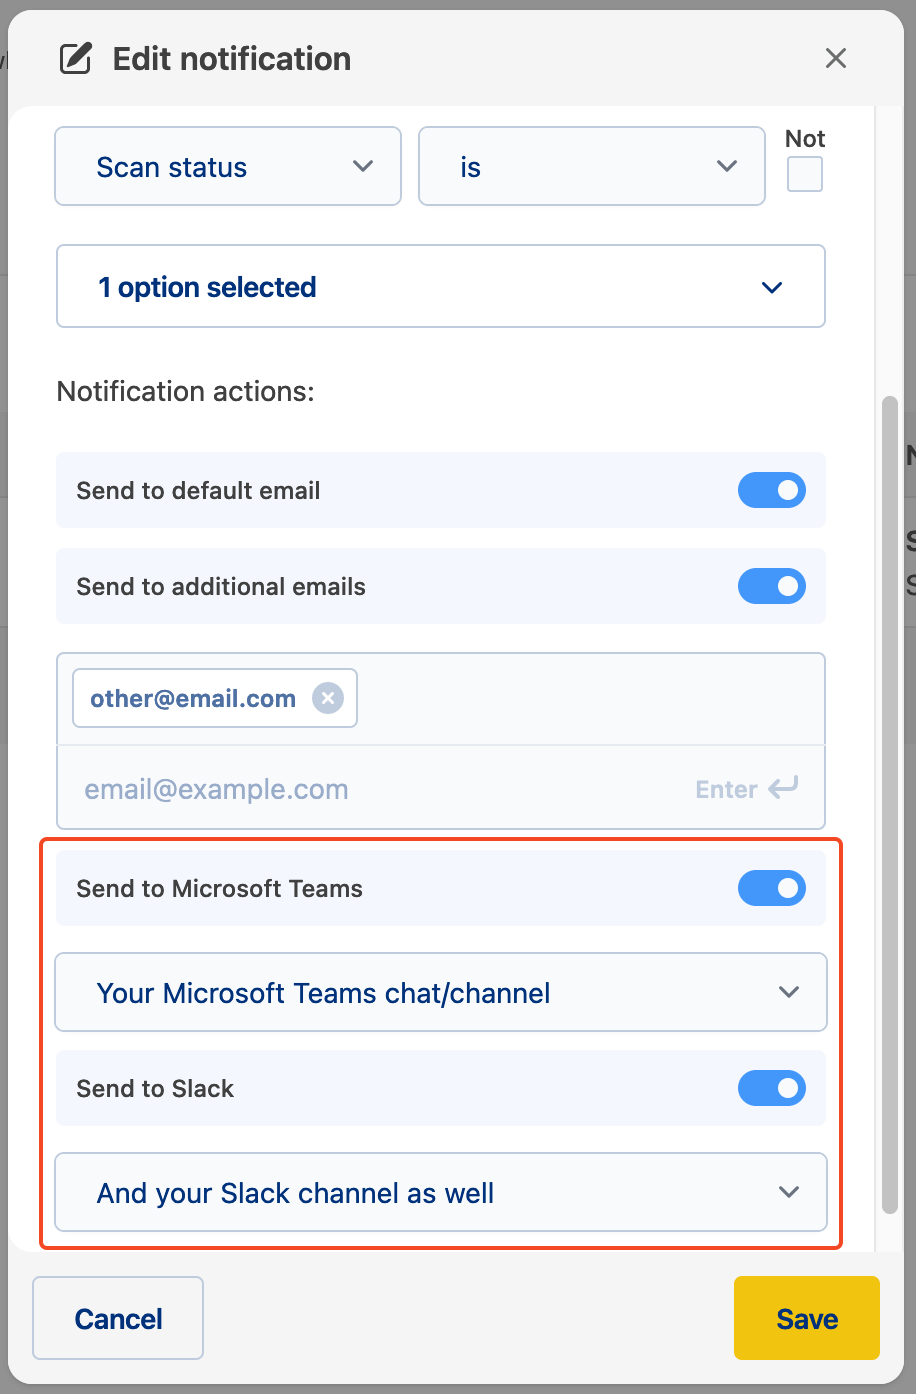
    • Unified notifications across integrations: you can now get the same notification through multiple services, in preparation for even more integration options we’ll launch in the future.

    multiple integrations

March 2024

  1. Don’t miss a thing with new detection modules in the Network Scanner

    Copy link to “Don’t miss a thing with new detection modules in the Network Scanner”

    Thanks to our security research team, you can now detect:

    Speaking about Roundcube, a couple of months ago we published an analysis - and public exploit - for CVE-2021-44026, an SQL injection vulnerability in the open-source mail client.

    The Network Scanner now also generates explicit findings for sensitive services that shouldn't be exposed on the internet (e.g. SMB, RDP, MySQL), which are easier to include in your reports.

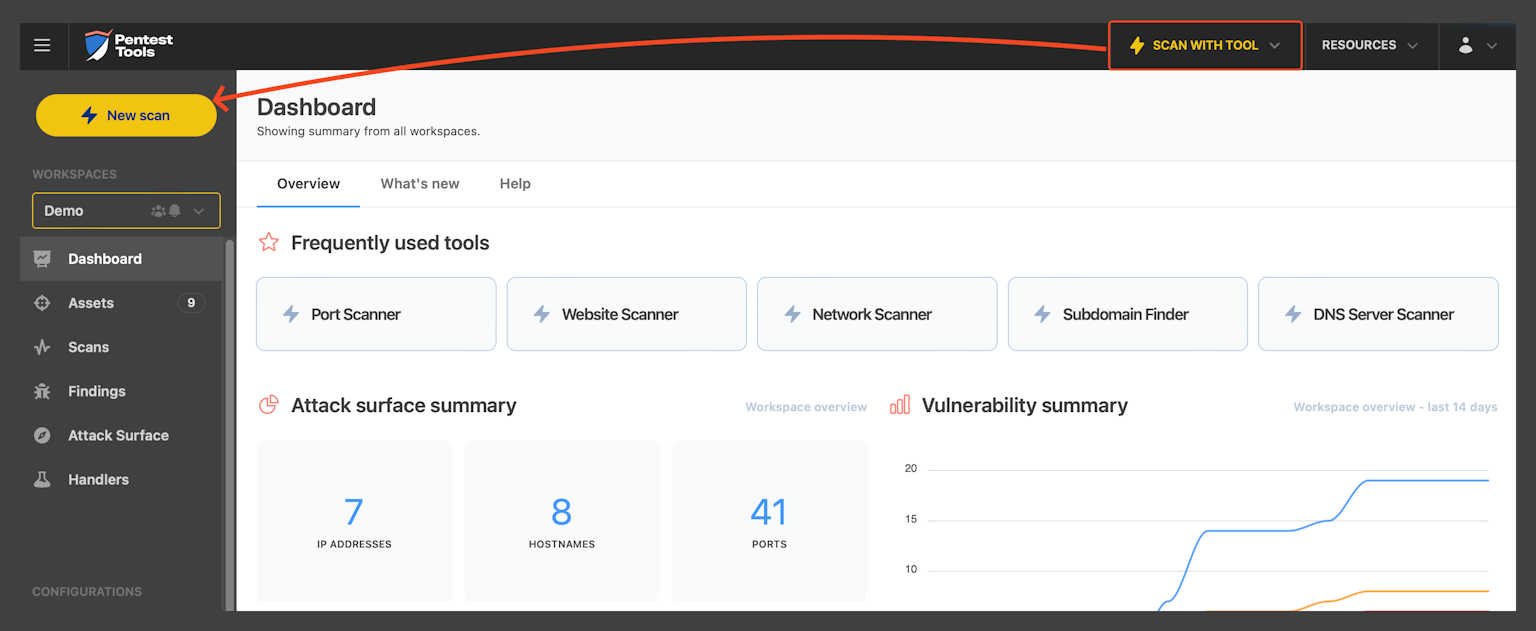
  2. The Scan with Tool button has a fresh look and a new location. It's now called New Scan and you’ll find it at the very top of the sidebar. We are working to make your scanning experience even better in the future!

    Scan with Tool button

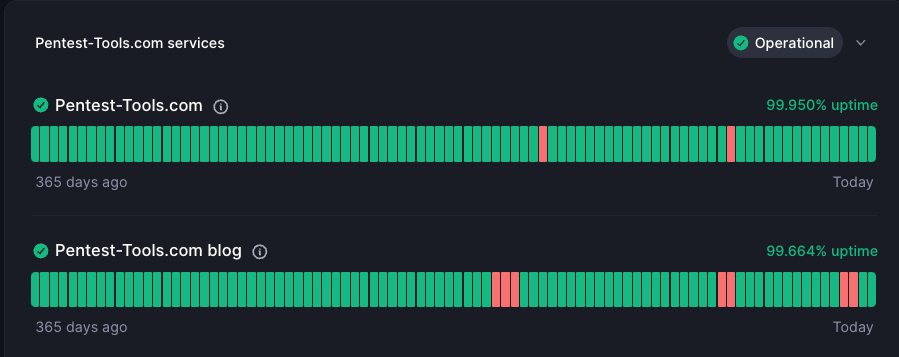
  3. This is something we promise you’ll always see in our new status page. 🤞The page includes statuses for our public website, the blog, the platform, the API, and more!

    services status

  4. Is Pentest-Tools.com any good for bug bounty hunting?

    Copy link to “Is Pentest-Tools.com any good for bug bounty hunting?”

    See what happens when The XSS Rat combines his methods with our toolkit and features.

    PS: Sniper Auto-Exploiter gets a lot of love - and for good reason!

    Bug Bounty Hunting Demo With Pentest-Tools.com - SuperCharge Your Hunt!
  5. New tool: know your targets better with People Hunter

    Copy link to “New tool: know your targets better with People Hunter”

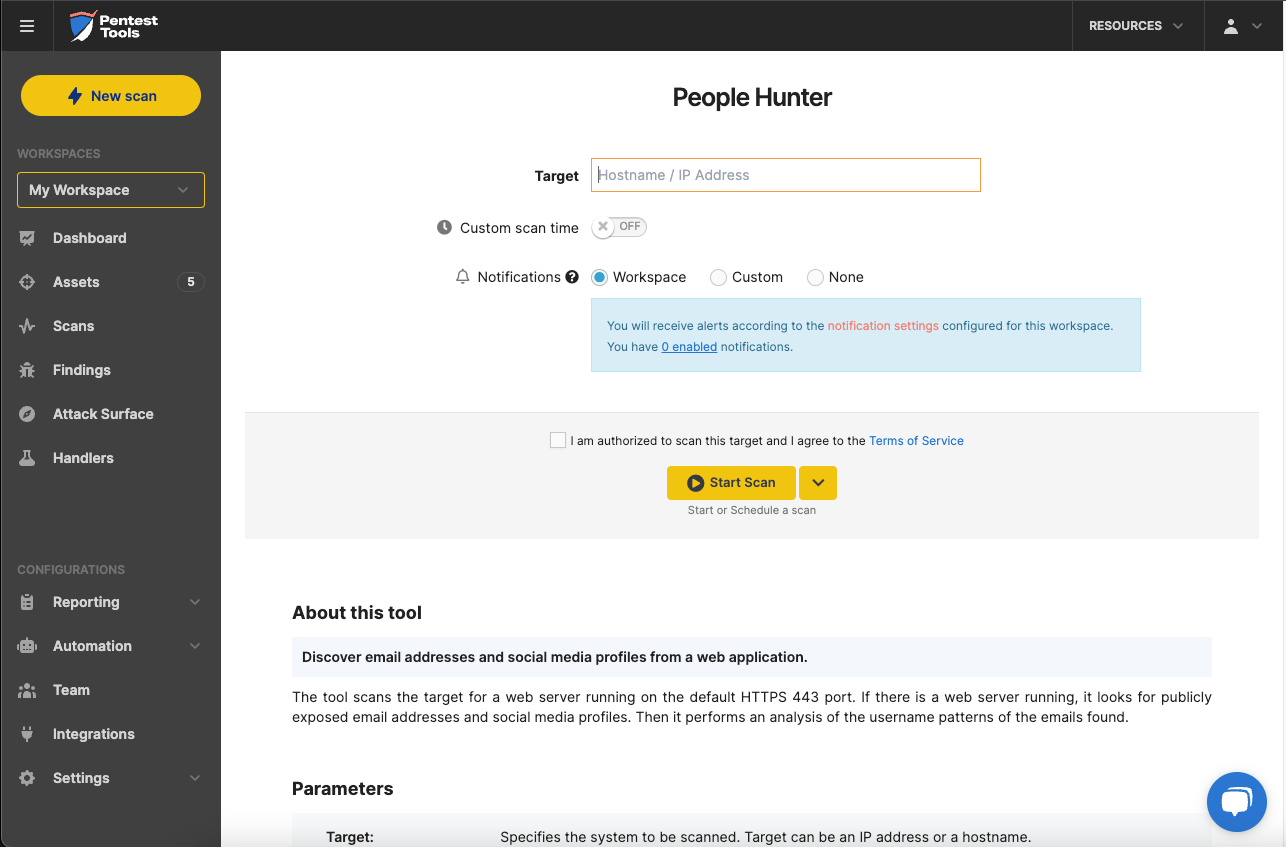
    People Hunter identifies the people associated with the target, using publicly available information from web server responses.

    Details such as email addresses (and their patterns) and social media profiles help you identify potential targets for social engineering attacks.

    People Hunter tool

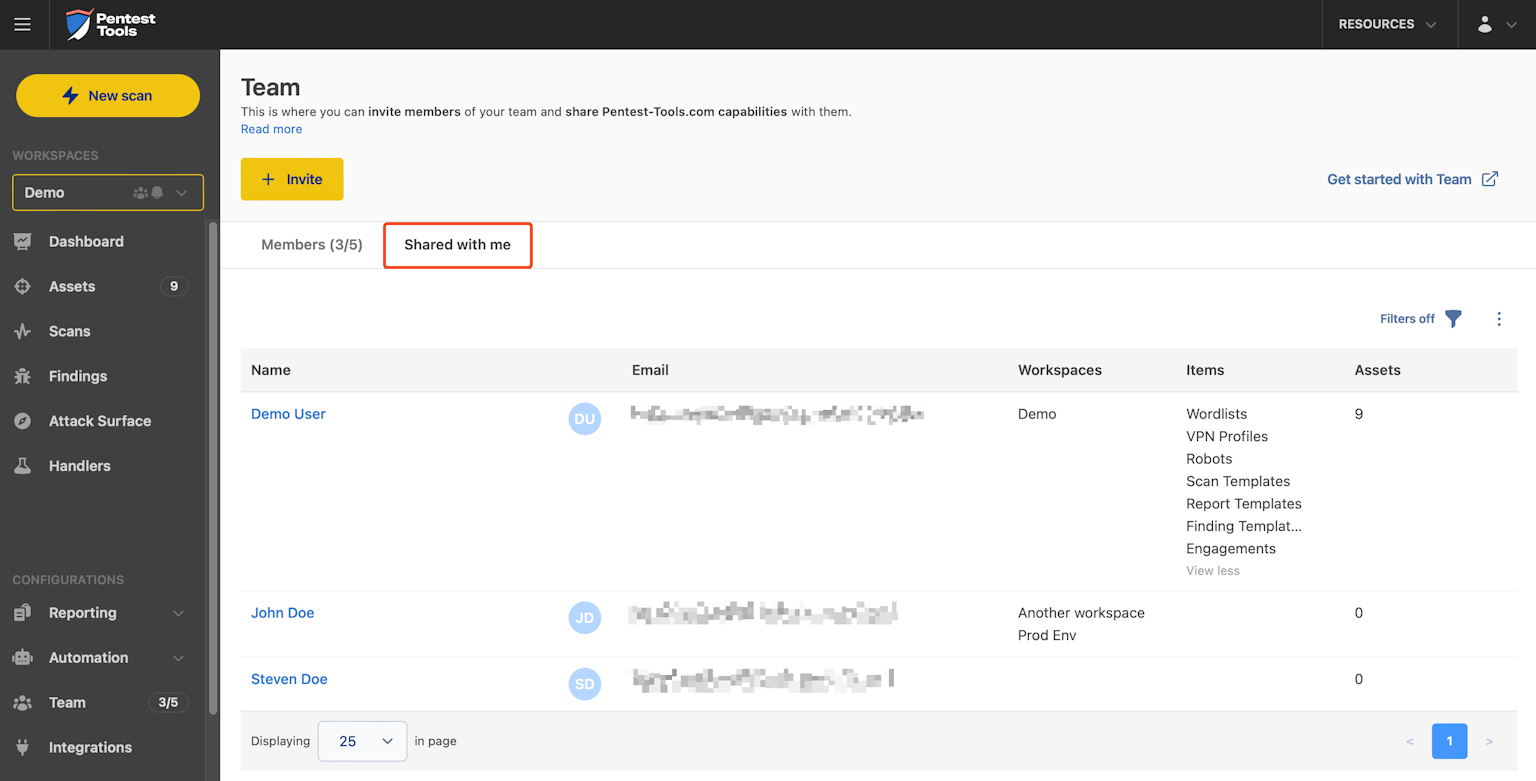
  6. We introduced a new view in the Team feature: Shared with me to help you identify who has shared which information with you. Additionally, the table view has returned, making visual comparisons easier.

    Shared with me in the Team page