
Pricing
AI Pentests
Autonomous AI web application and API pentesting - scalable, on-demand.
Discover complex, multi-step vulnerabilities
Exploit each vulnerability to prove the risk
Run black-box or grey-box (authenticated) testing
Test remotely as an attacker, no source code required
Get audit-ready reports for SOC 2, ISO 27001, NIS2, HIPAA, etc. compliance needs
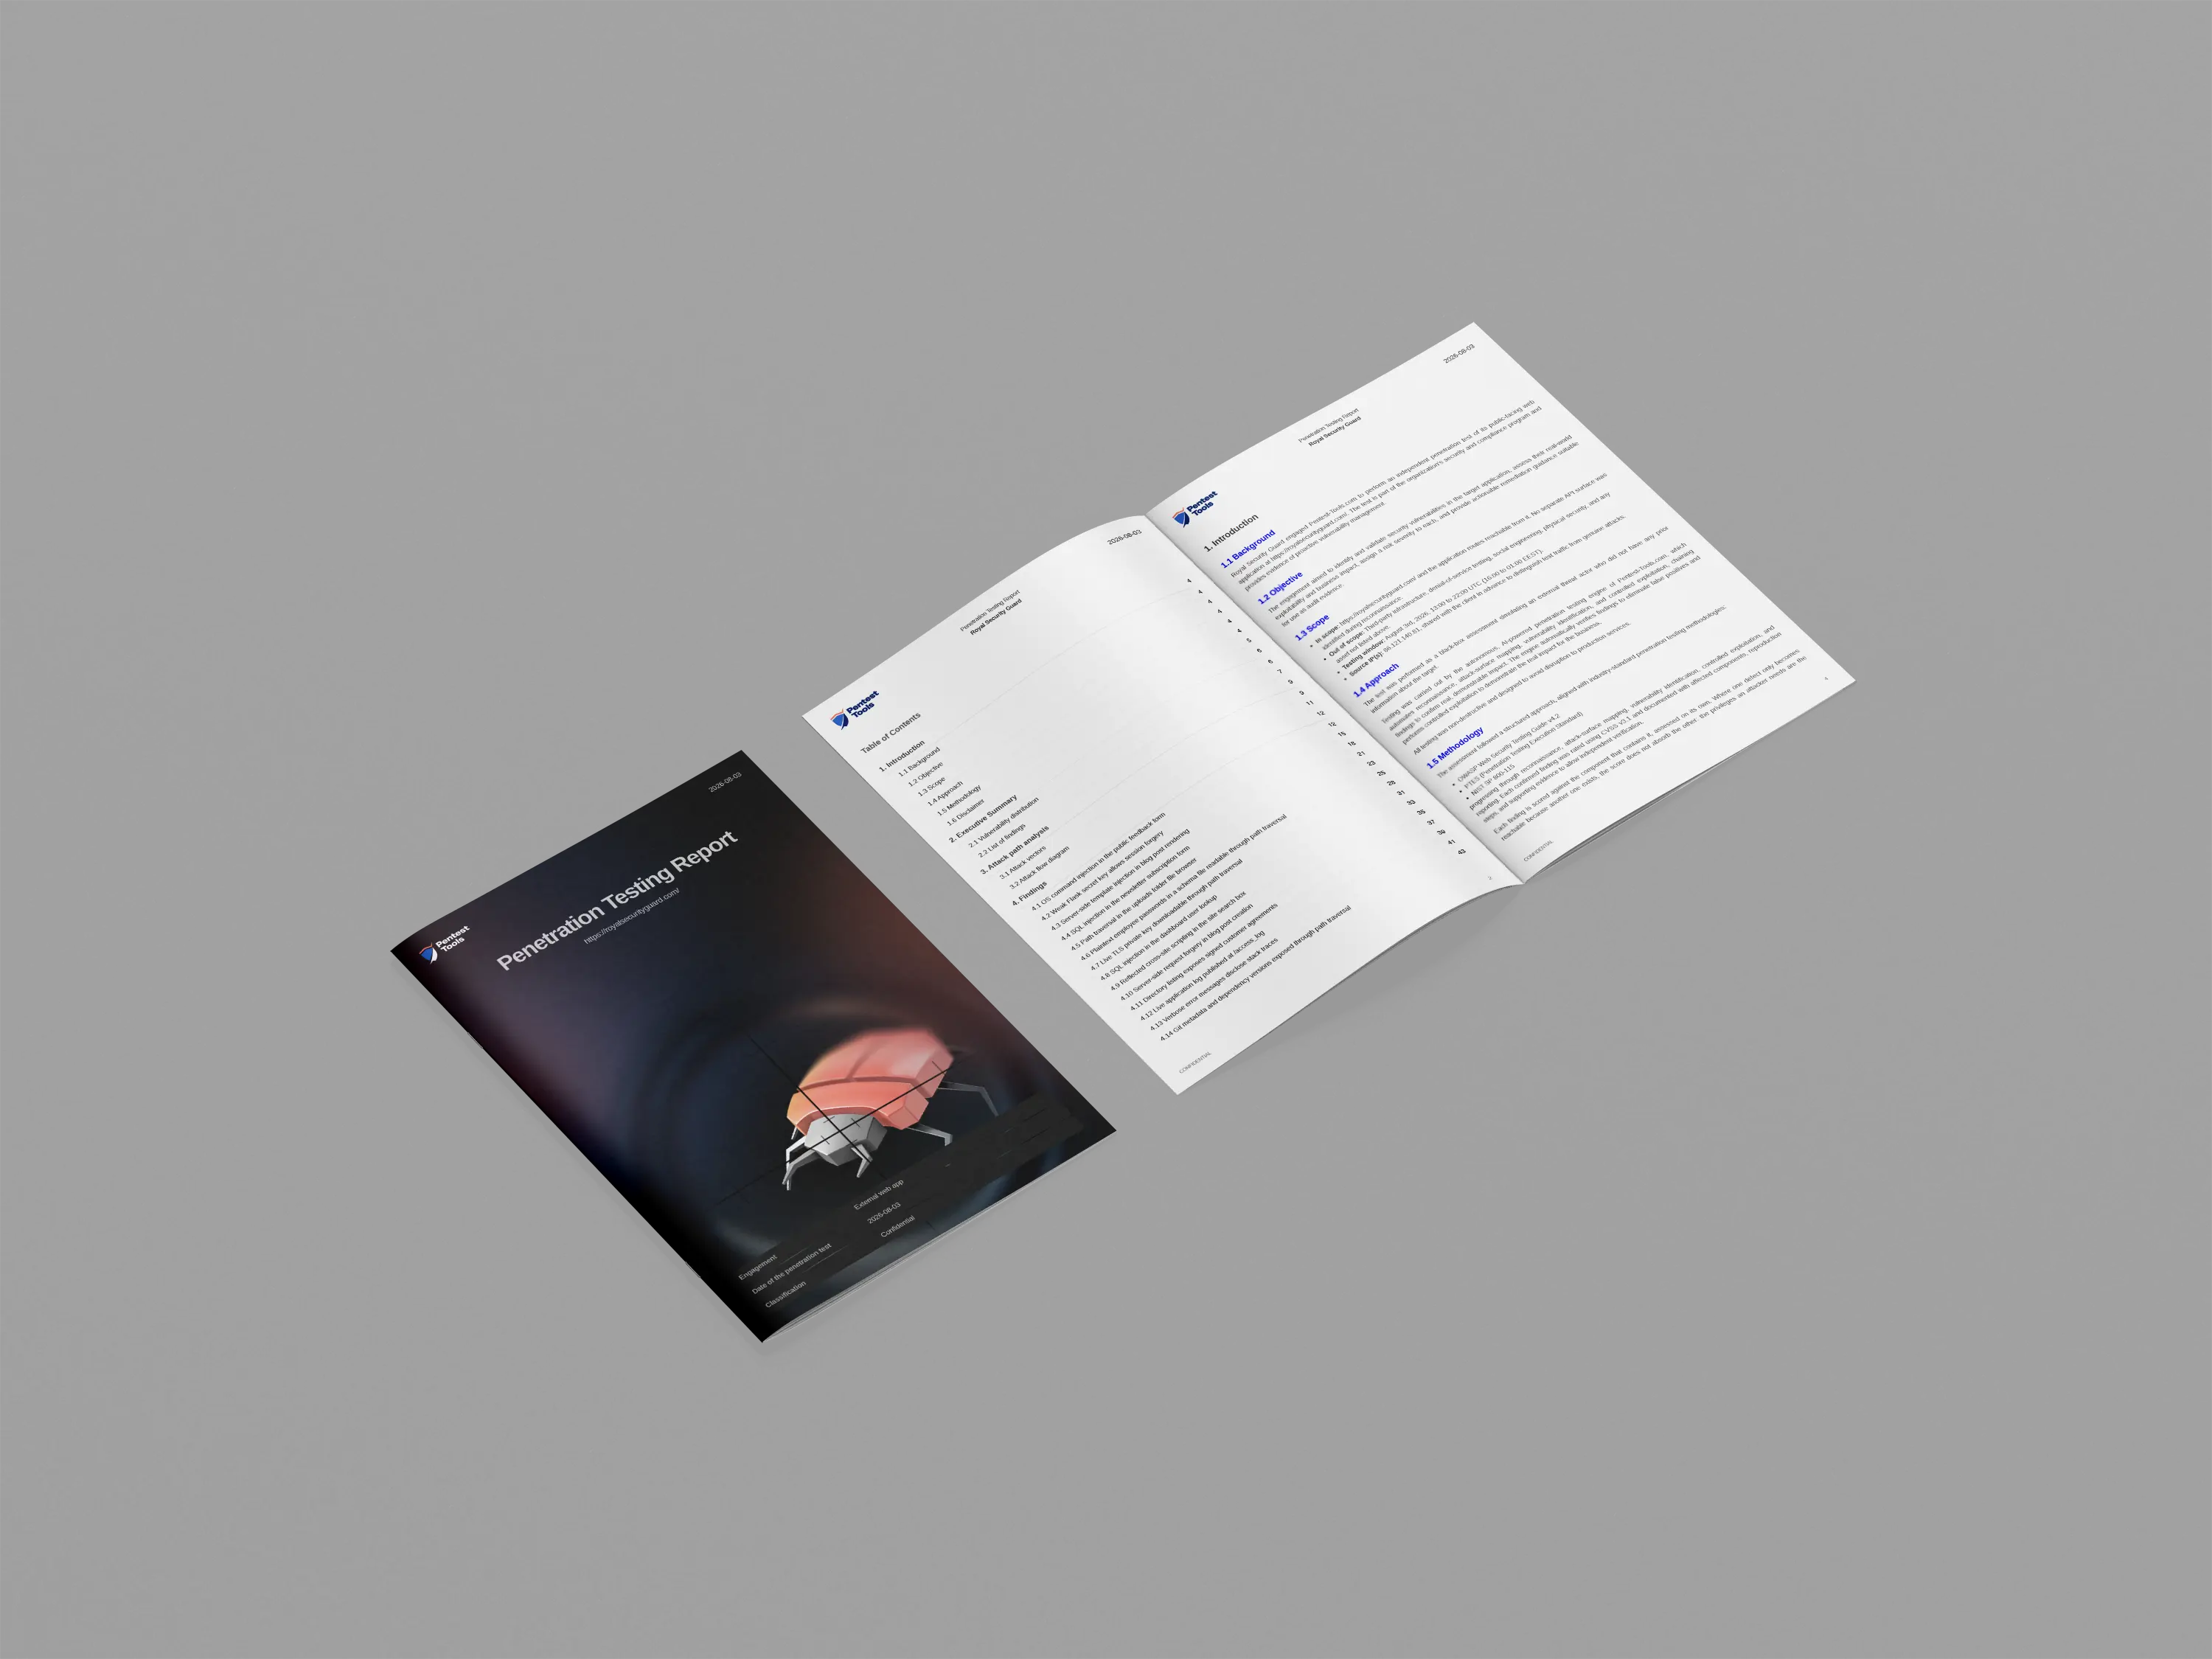
Audit-ready reports, on demand
Confirmed exploitable findings with reproducible evidence, plus an executive summary that translates results for leadership. Structured to hold up for SOC 2, ISO 27001, NIS2, HIPAA, and other major audits.
FAQ
You have questions, we're here to clarify
What kind of web application pentest does it execute?
Black box by default. Give it credentials or API token details through the Agent instructions, and it runs grey box, signing in and testing authenticated flows.
Do I need to give you access to my source code?
No. AI Pentests works from your web app's URL. No repo connection required to get started.
How is this different from other AI pentesting tools?
Most require connecting your GitHub or GitLab to reach full depth - which makes cost hard to predict before you run a test. AI Pentests works from the URL and fits a team testing more than one environment on its own schedule.