Changelog

These are the latest updates we've made to our platform. If you have any questions about any of the updates you see below, please feel free to contact us!

Date

March 2024

  1. Two new modules in the Website Vulnerability Scanner

    Copy link to “Two new modules in the Website Vulnerability Scanner”

    Two new modules in the Website Vulnerability Scanner:

    • Detection for misconfigured CSP Headers - identifies misconfigured content-security-policy headers on your website, enabling you to control resource loading and their allowed URLs.

    • Enumerable Parameter Detector - explores possible enumerable parameters in your website. Some findings might reveal insecure direct object references after manual examination.
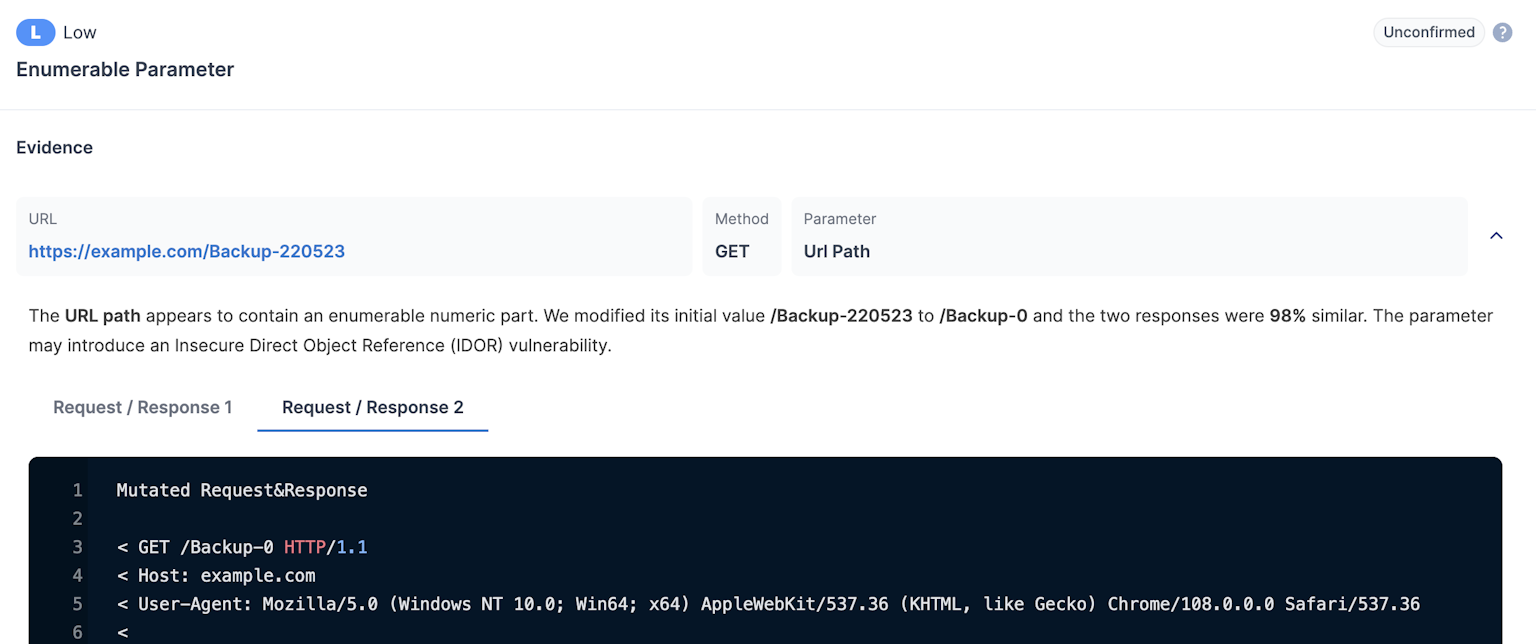
    enumerable parameter detector

February 2024

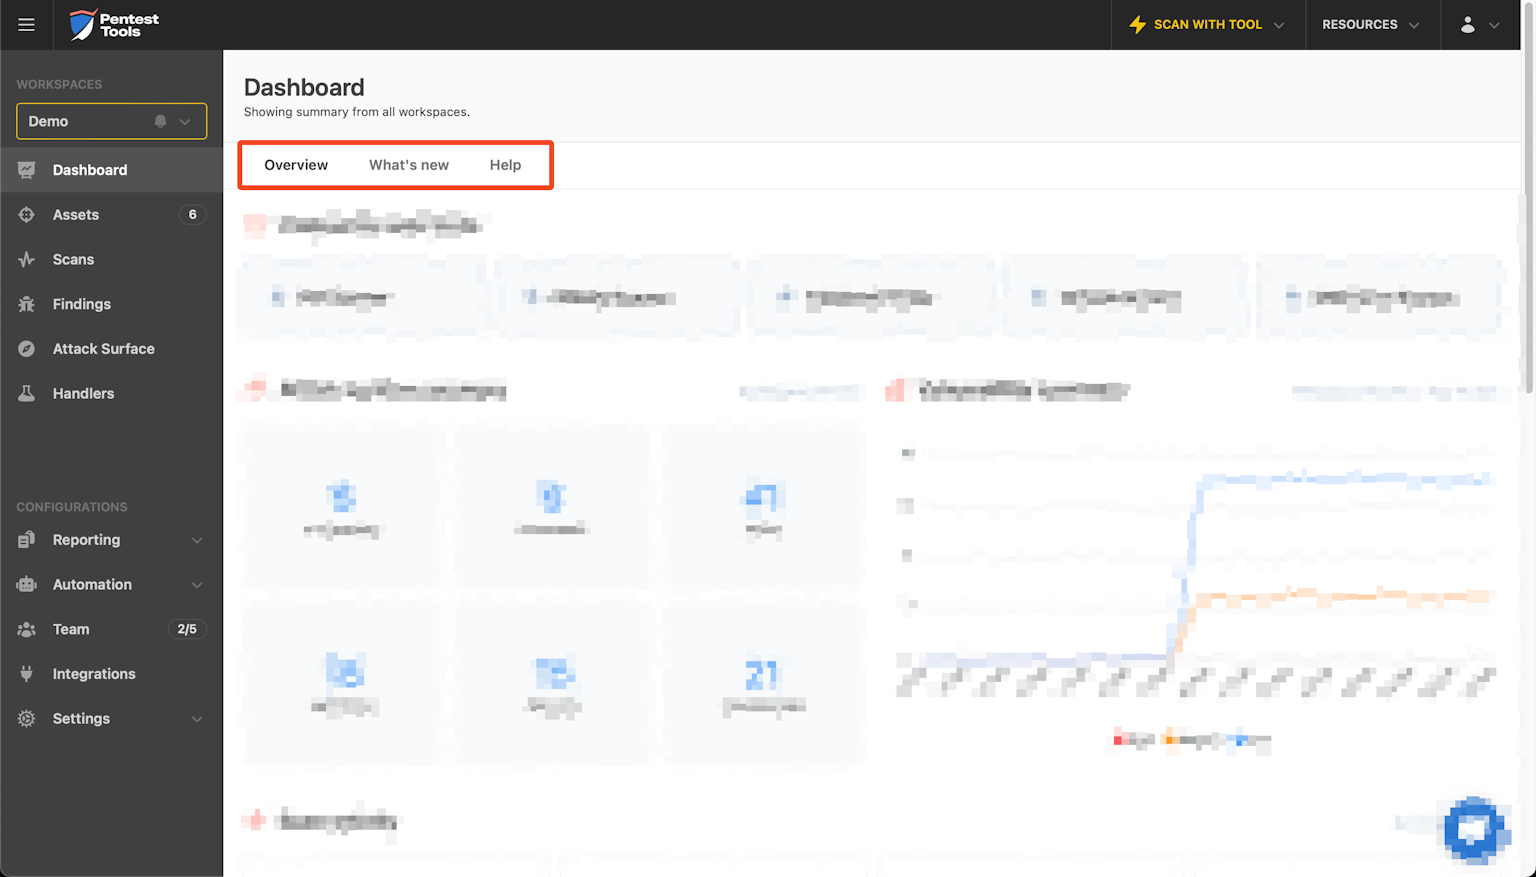
  1. Know what’s new - right from your dashboard

    Copy link to “Know what’s new - right from your dashboard”

    Until a few days ago, our product updates were a bit hidden from view, which made it harder for you to find out about them and actually use them.

    So we added two new sections to your dashboard:

    • What’s new - that brings product updates (text and video) and fresh pentesting guides

    • Help - which makes it easier to dip into how-to’s, video tutorials, and FAQs

    New dashboard

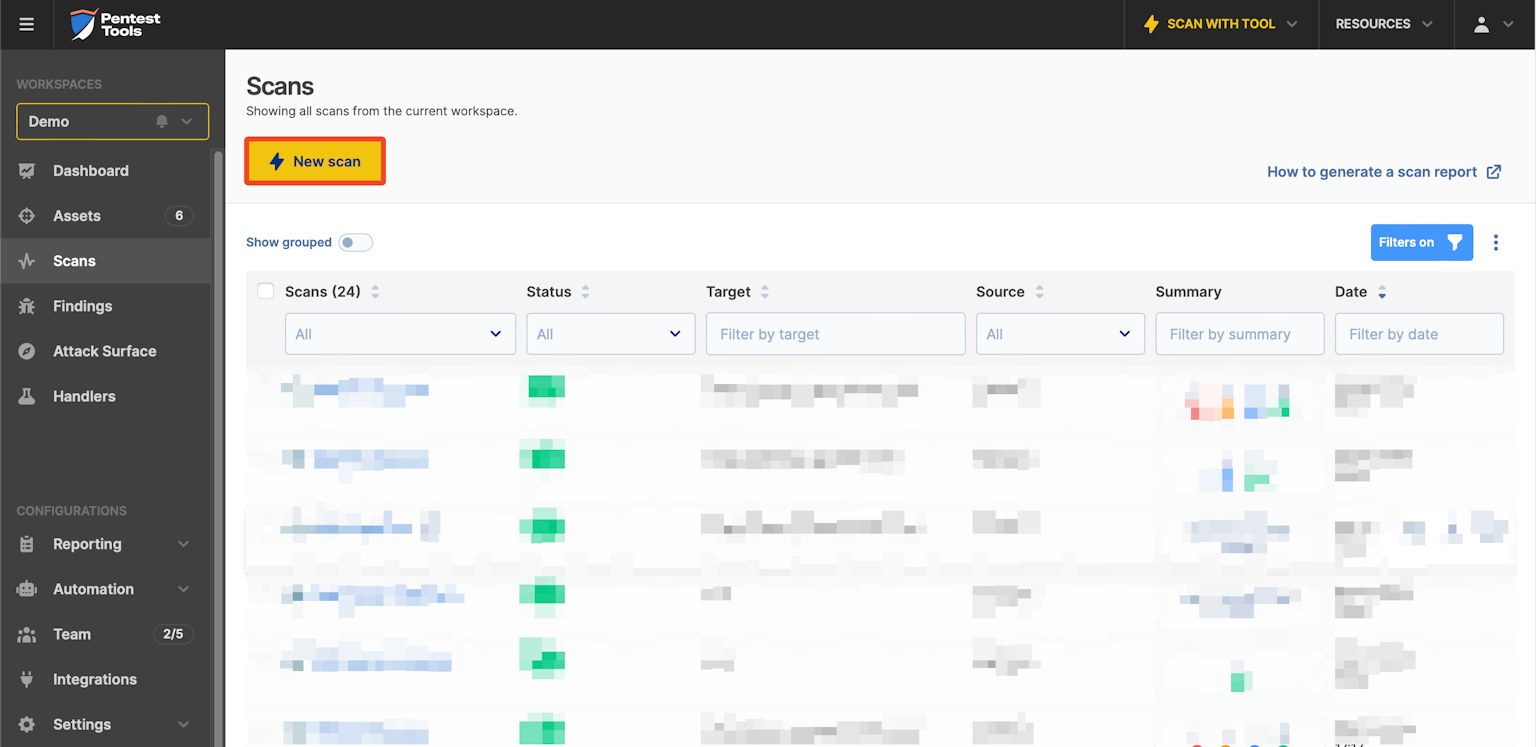
  2. We noticed some of our customers needed an easier way to start scans from the (obviously named) Scans section, so we added it!

    The New scan button makes it easy to jump into action the moment you know where you want to dig deeper.

    New scans button

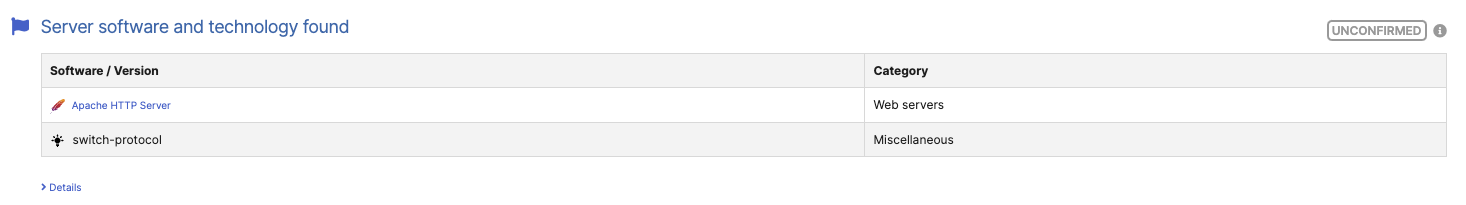
  3. Nuclei fingerprinting in our Website Scanner

    Copy link to “Nuclei fingerprinting in our Website Scanner”

    Our Website Vulnerability Scanner gets stronger with each monthly update!

    We’ve integrated the fingerprinting capabilities from Nuclei into our proprietary tool - and it’s just the kickoff!

    Soon, we’ll start incorporating many more templates. Until then, the 40+ vulnerability checks our Website Scanner runs can surely keep you - and your team - focused and making progress.

    Nuclei fingerprinting

  4. More Nuclei detections in the Network Scanner

    Copy link to “More Nuclei detections in the Network Scanner”

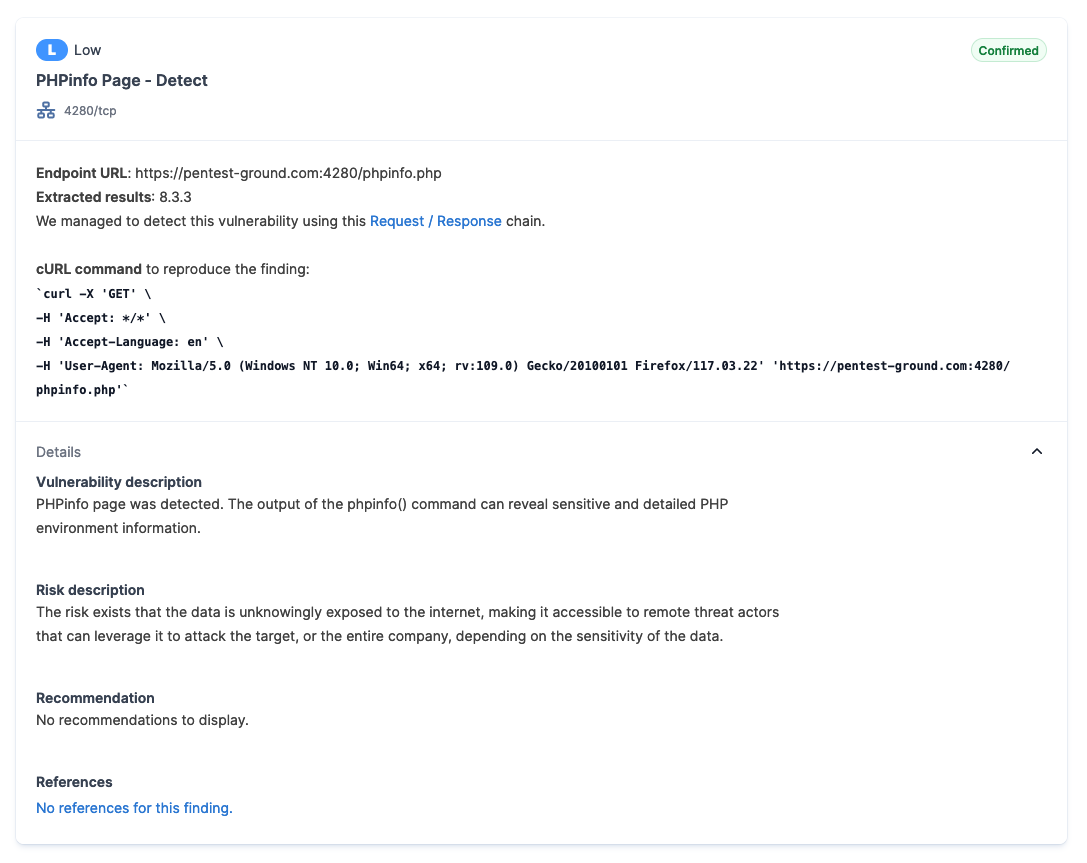
    We’ve also integrated a bunch of new Nuclei category templates on top of the configured ones our Network Scanner is already using (CVE, CNVD, SSL, network, WAF, DNS).

    New ones include: default-logins, exposed-panels, exposures, honeypot, IoT, miscellaneous, misconfiguration, takeovers, and vulnerabilities.

    Want to refresh your knowledge of what our Network Vulnerability Scanner can do? We just updated its public page:

    Nuclei in Network Scanner

January 2024

  1. New integration: get notifications on a Teams channel

    Copy link to “New integration: get notifications on a Teams channel”

    If you (and your team) use Microsoft Teams, set up this integration to get custom notifications for your scan results.

    You can also configure different channels for specific notifications, making sure everyone gets alerts about findings that are relevant for them.

    Microsoft Teams integration

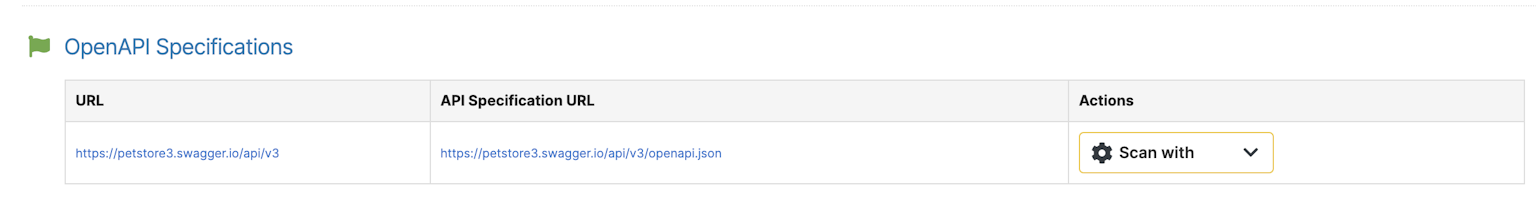
  2. And one more thing: we added a method to detect if the Website Scanner spider finds an OpenAPI file. When it does, you can dig deeper with the API Scanner in just one click, right from your finding.

    OpenAPI file detection

    By the way, we love to see customers truly make the most of our tools:

    We had a tool to scan our websites and endpoints automatically; the reports were not so good, and each additional URL was charged additionally (this doesn't scale in a micro-services architecture).

    Pentest-Tools.com solved all our problems; you can scan up to 1000 targets, the reports are so professional, and you can choose from dozens of different tools to analyze all aspects of an enterprise architecture.

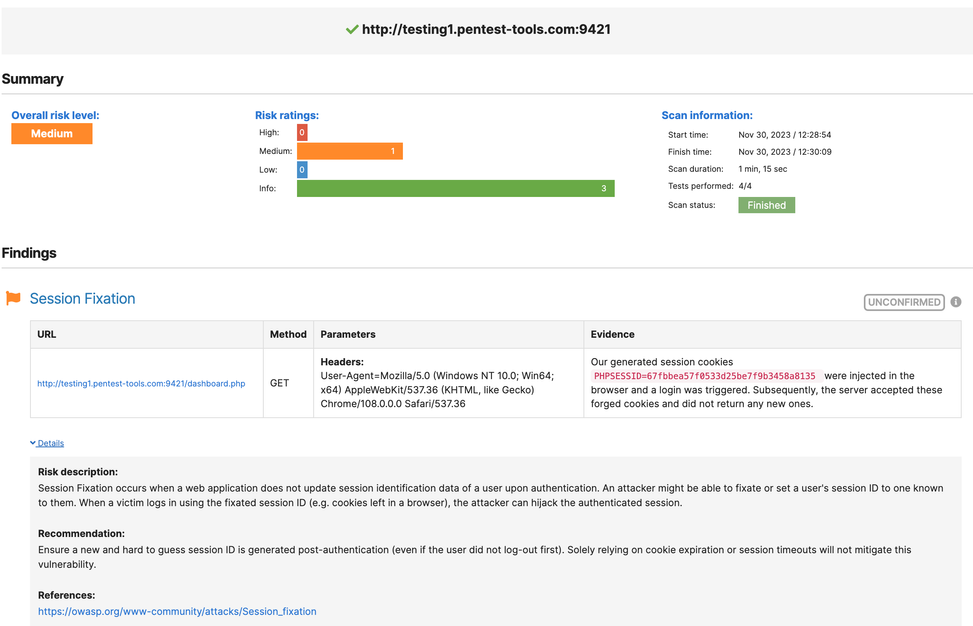
  3. We've also introduced a new Session Fixation Detector to help you identify session hijacking risks. Using the mitigation recommendations will help you prevent unauthorized access to user sessions and sensitive data.

    Here’s a preview of what the finding looks like:

    session fixation finding

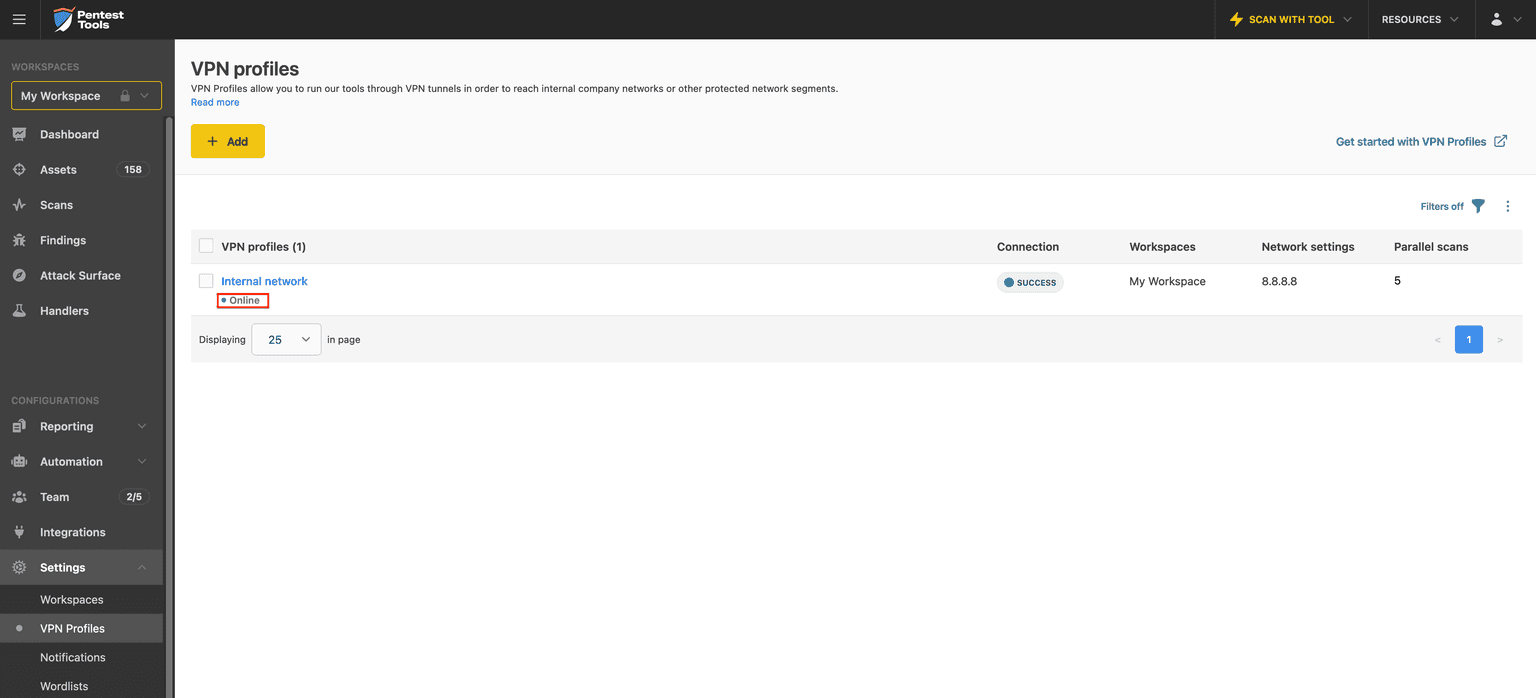
  4. Real-time status for all your VPN Agents

    Copy link to “Real-time status for all your VPN Agents”

    You can now check the status of your VPN Agents in the VPN Profiles section (under Settings).

    We update their status in real-time, which makes it easier for you to check if your Agents are still up and running before starting scans against your internal infrastructure.

    VPN Agent status

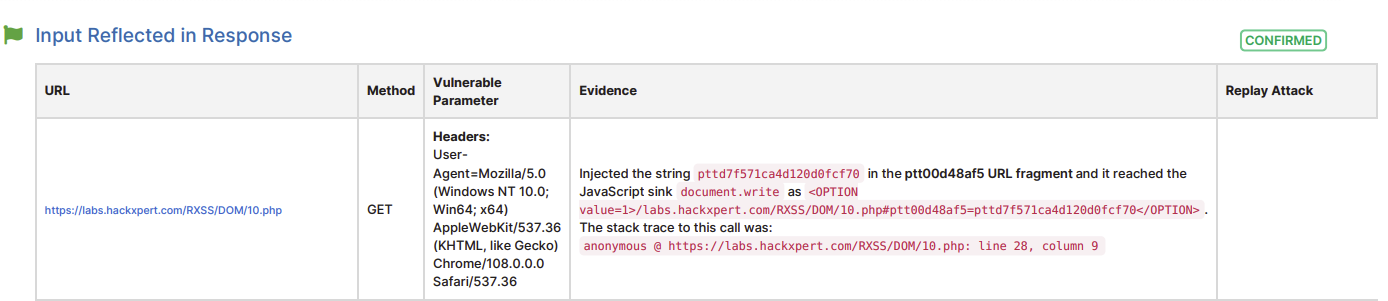
  5. We've implemented Input Reflected in DOM to enhance protection against XSS attacks, ensuring coverage of more vulnerabilities lying in the DOM. It is already implemented in the XSS detector so if you select the XSS detector you are covered.

    Here’s what it’ll look like in your report:

    Input Reflected

December 2023