
CVE scanner for critical vulnerability response
When a critical CVE like PHP2Shell drops, the first question is "does this affect us?" Pentest-Tools.com helps you answer it with evidence, prove it where possible, and confirm the fix.
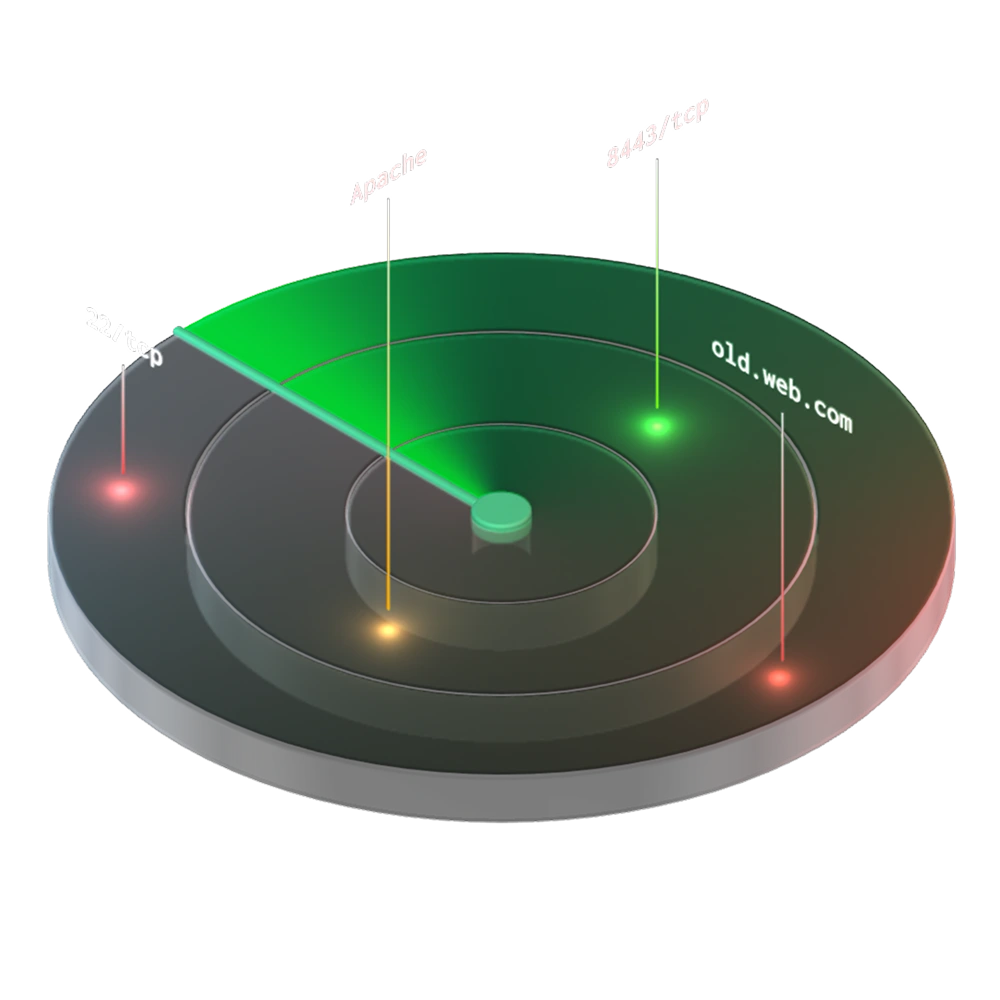
Our Network Vulnerability Scanner works as a CVE scanner with 17,500+ detections, active and version-based, including new detections our research team builds and tests in-house for high-profile CVEs.
When we build an exploit module, Sniper takes you one step further and shows which systems an attacker could compromise.
Critical CVEs we’ve covered
Why a version match doesn't settle your exposure to a critical CVE
A matching software version only flags potential exposure to CVEs like PHP2Shell or Node2Shell. You still need to find affected systems, confirm the vulnerability, determine if attackers can exploit it, and verify the fix.
Version strings can mislead you in both directions. For example, Linux distributions often backport PHP fixes without changing the version number, so a PHP2Shell version match can flag an already patched server. And a server that hides its PHP version won’t show up in a version check at all, even if it’s still vulnerable.

Escalating without proof costs credibility
Raise the alarm on a version guess, and engineering rushes to patch something that wasn't exploitable. Stay quiet on the same guess, and leadership hears about the exposure from someone else.
Answering without evidence will create more frustration than dropping everything to put out a fire like React2Shell.

Patching doesn't prove the gap closed
You patch the production instance you remember first. The staging copy, the container image built last quarter, or the site a former colleague set up often stays exposed.
HTTP2Shell shows how this happens: the vulnerable decoder ships inside the Node.js runtime, so a patched host can still run containers built on the old one.
Until you re-test, "we patched" remains an assumption.

For MSSPs, the same question comes from every client
Each client expects an answer today. Each answer pulls an analyst off billable work, and each delay risks a client finding out from the news first.
And the next critical CVE is rarely far behind.
How we ensure efficient response to critical CVEs
17,500+ CVE detections · Emergency detections tested in-house · Single-CVE scanning · Reliable exploit validation where available · 210+ Sniper exploit modules
From critical CVE to verified fix
Our response to a critical CVE comes in two layers, and you can use the first one as soon as it ships.

Network Scanner detection, in every paid plan
As soon as our research team has a check it trusts, it goes into the Network Vulnerability Scanner. Each detection works in one of two ways:
Active detection tests how the target behaves. For Node2Shell, the scanner checks whether an endpoint decodes Brotli with a vulnerable decoder, without running code on the server.
Version-based detection flags software in the vulnerable range when the target discloses its version. The report says which method produced each finding, so you know how much weight it carries.
Every finding includes the request and response behind it, so you can check the evidence yourself.

Exploit validation with Sniper, where available
For selected CVEs, our researchers also build an exploit module for Sniper: Auto-Exploiter.
Depending on the vulnerability, Sniper extracts proof such as the current user, system information, local users, running processes, network configuration, and interesting files from the filesystem. This is how Pentest-Tools.com supports Adversarial Exposure Validation.
Exploit modules take longer than detections, because a reliable exploit has to work across the affected variants. For Node2Shell, detection shipped on October 25, 2026, and the exploit module followed on October 29.
Here's how both layers fit into your response
1. Target the CVE
Run a single-CVE scan across your assets.
2. Confirm exposure
Review the evidence behind each detection, active or version-based.
3. Prove exploitability, where available
Run the matching Sniper module to see what an attacker could do on that target.
4. Verify the fix
Re-scan after patching to confirm the vulnerability is gone.
5. Stay covered
Schedule scans to pick up new detections automatically.
Need to check a critical CVE now?
Emergency CVE detections come with every paid plan, and exploit validation comes with our most comprehensive plan.
Critical CVEs we've covered
Every CVE below allows unauthenticated, remote attacks, and our team tested each emergency detection in-house before release.
Where we shipped an exploit module, Sniper can, depending on the vulnerability, gain command execution, read sensitive files, extract proof of compromise, and map the target's network, making the attack chain visible and verifiable.
| Released | CVE | Vulnerability type | What we shipped |
|---|---|---|---|
| Oct 2026 | PHP2Shell (CVE-2026-109618, CVE-2026-109619) | Remote code execution in PHP core, exploited before a fix existed | Detection (version-based, then active) |
| Oct 2026 | Node2Shell / HTTP2Shell (CVE-2026-111497) | Out-of-bounds write in the Brotli decoder in Node.js, Bun, and Envoy | Detection + exploit |
| Jul 2026 | wp2shell (CVE-2026-60137, CVE-2026-63030) | WordPress core SQL injection chain to remote code execution | Detection + exploit |
| Feb 2026 | Ivanti EPMM RCE (CVE-2026-1281) | Unauthenticated code injection in Ivanti Endpoint Manager Mobile | Detection + exploit |
| Feb 2026 | GNU Inetutils telnetd authentication bypass (CVE-2026-24061) | Remote root access without a password | Detection + exploit |
| Dec 2025 | React2Shell (CVE-2025-55182) | Remote code execution in React Server Components and Next.js | Detection + exploit |
| Nov 2025 | Oracle E-Business Suite RCE (CVE-2025-61882) | Pre-auth remote code execution in Oracle EBS 12.2.3 to 12.2.14 | Detection + exploit |
| Oct 2025 | Magento SessionReaper (CVE-2025-54236) | Session and account takeover in Adobe Commerce and Magento | Detection + exploit |
A fast answer only helps if it’s accurate
Speed matters in the first days after a critical CVE goes public. But an answer that turns out wrong creates a second emergency: a false alarm that burns trust with engineering, or false reassurance that leaves a door open.
That’s why we focus on ensuring both speed and accuracy with thorough in-house testing.

Exploitation depth built in-house
210+ exploit modules in Sniper, written and tested by our offensive security research and product teams
First place for remote detection accuracy
Highest remote detection accuracy across 128 vulnerable environments in our network scanners benchmark

Tested by our team, every time
Before we launch an emergency detection or exploit module, our offensive security experts test it in a lab against vulnerable and patched versions of the affected software.
That testing is one reason some releases take longer than others. How complex a CVE is, and when it drops (weekends included), also shapes how fast a detection or exploit module ships.
How we choose which CVEs get an emergency response
We’d rather spend a bit more time developing a reliable detection or an exploit than release one that sends your team after false positives.
That’s why our research team weighs several factors when a critical vulnerability emerges:
Vulnerability severity and impact, with a focus on critical remote code execution and authentication bypass
If attackers can exploit it remotely, without credentials or user interaction
A public proof of concept or confirmed exploitation in the wild
How widely the affected software runs on internet-facing systems
How Pentest-Tools.com helps each team respond to critical CVEs
Exposure and exploitability are two different layers. Exposure checks if the vulnerable code runs on your systems. Exploitability confirms if an attacker could use it there, given your configuration and defenses.
We help teams cover both - with accurate proof, remediation steps, and ongoing vulnerability monitoring across web, network, and cloud assets.
| Internal security teams | MSSPs | IT teams |
|---|---|---|
| Answer leadership with an evidence-rich report | Check exposure across client environments, quickly and accurately | Determine exposure to critical CVEs without dedicated resources |
| Prove exploitability before escalating to engineering | Deliver client-ready evidence that stands up to questions | Follow clear remediation steps without a specialist on call |
| Verify the patch held with a re-scan of the same CVE | Protect billable time with evidence that cuts manual triage | Confirm you’re done with a re-scan after patching |
| Add Adversarial Exposure Validation capabilities to the internal security program | Start the next CVE from coverage with scheduled scans | Keep the evidence your compliance obligations ask for |
Be ready before the next critical CVE drops
Emergency CVE detections come with every paid plan, and exploit validation comes with our most comprehensive one.
Choose the plan that fits your team, or book a demo to walk through a CVE response with one of our colleagues.
Emergency CVE response FAQs
Here's what teams ask us most when a critical CVE is on the line.
How quickly do you add detection for a new critical CVE?
It depends on how complex the CVE is and when it drops. For PHP2Shell, version-based detection went live on October 21, 2026, hours before PHP released its fix, and active detection followed the next day. For Node2Shell, detection shipped three days after the CVE went public and two days before CISA added it to the KEV catalog.
Exploit modules take longer, because we develop and manually test each one before it reaches you. The Node2Shell exploit module shipped four days after its detection.
How do you decide which CVEs get an emergency response?
Our offensive security research and product teams prioritize critical CVEs that attackers can exploit remotely without credentials, especially when a proof of concept is public or exploitation has been confirmed, and when the affected software runs widely on internet-facing systems.
Is emergency CVE detection included in my plan?
Emergency detections come with every paid plan. Sniper exploit validation comes with our most comprehensive plan. Our pricing page always has up-to-date information on plans and prices.
What's the difference between detection and exploit validation?
Detection determines exposure. Active detection tests whether the target shows the vulnerable behavior. Version-based detection flags software whose disclosed version falls in the vulnerable range.
Exploit validation with Sniper safely reproduces the attack and attaches artifacts that prove an attacker could use it, which determines exploitability. Depending on the vulnerability, Sniper can gain command execution, read sensitive files, extract proof of compromise, or map the target's network. That shows you what an attacker could do with that specific CVE in your environment.
For example, the GNU Inetutils telnetd module returns a root shell banner. The Magento SessionReaper module captures session takeover evidence.
Is it safe to run these checks against production systems?
Emergency detections don’t run code on your server, and each one documents its side effects before you scan. For example, the Node2Shell check uploads about 23 MB to endpoints that decode Brotli, and the larger PHP2Shell probes can use a lot of memory and may stop the PHP worker that receives them.
Sniper exploit modules run in a controlled, non-destructive way and attach the evidence they collect to the finding.
If you'd rather keep production out of it during a live incident, start with a detection-only scan. Then run Sniper against a staging copy of the affected system.
As with any testing, scan and exploit only assets you're authorized to test.
How do I scan for just one CVE?
In the Network Scanner, start a custom scan, open Engine options, choose Select CVEs, and enter the CVE ID. The scan checks only that vulnerability across the targets you include.
Will my scheduled scans pick up new detections automatically?
Yes. Scheduled scans include new detections on their next run, and alerts fire only on new findings, by email, webhooks, Slack, or Microsoft Teams.
What does an "Unconfirmed" result mean for a critical CVE?
It means the software version sits in the vulnerable range, but the scan didn't validate exploitability. Patching remains the right action.
Where a Sniper module exists, you can use it to settle whether the CVE is exploitable in your environment.
What if a CVE I care about isn't covered yet?
Watch the Vulnerabilities & Exploits Database, the changelog, and our LinkedIn for announcements for new emergency detections. Customers are the first to get an email when we ship a new emergency detection or exploit module.
Can I share the results with leadership or clients?
Yes. Every scan produces either a vulnerability assessment report (PDF, HTML, CSV, XLSX, JSON) or a pentest report (PDF, HTML, DOCX, Google Docs) with findings, evidence, and remediation steps, in the formats your plan includes. MSSPs can deliver it as a client-ready report with branded reports and emails.
Does a version check tell me whether I'm exposed?
A version check tells you the software falls within the vulnerable range. Backports, mitigations, and configuration can change the real answer. That’s why we build active detection wherever we can, and why the report labels version-based findings as such.
Want to check a specific CVE for free first?
For selected high-profile CVEs, we offer free single-CVE checks, such as the PHP2Shell scanner and the Node2Shell scanner. Find the rest in our emergency CVE scanners section.
Paid plans add the full loop: emergency detections, re-scans, and scheduled coverage for the next CVE, with exploit validation through Sniper on our most comprehensive plan.