Our offensive security research team found two authentication flaws in phpBB, one of the most widely deployed forum platforms on the web. Detection for CVE-2026-48611 is now live in the Network Scanner, and a working proof of concept for each is published in the research.
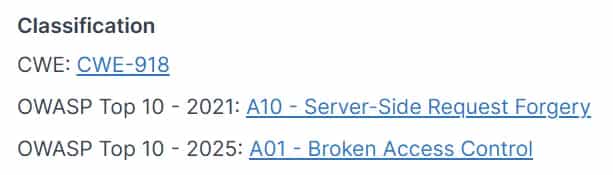
CVE-2026-48611 is a critical, unauthenticated authentication bypass (CVSS 9.4). One HTTP request with a target username and a wrong password phpBB never checks returns a valid session cookie for that account, admins included. It works on every default install up to and including phpBB 3.3.16, with no prior access needed. The vulnerable code path sat in the codebase for over a decade, surviving multiple major releases and security reviews.
CVE-2026-48612 is a high-severity OAuth account takeover (CVSS 8.3). It chains two OAuth defects for a silent takeover on boards with OAuth configured. In some cases the victim doesn’t click anything: an image tag embedded in a forum post is enough to trigger it.
Why it matters
A bypass that hands an attacker an admin session on a default install means full control of the board, its users, and whatever sits behind it. phpBB runs on countless community and corporate forums, so a single exposed instance is a foothold with real blast radius. We reported both to phpBB on June 4, 2026, and a fix shipped two days later in phpBB 3.3.17.
How to use
Detect CVE-2026-48611 with the Network Scanner, patch to phpBB 3.3.17, then re-scan to confirm the fix is in place and rule out residual exposure across multiple assets.
If the board has OAuth configured, audit the oauth_accounts table for unexpected entries after upgrading. A successful CVE-2026-48612 exploit leaves a record there.
Read the research